Author: Penny Marbel

  • CMMC Phase 2 Is Paused ,  Your Self-Assessment Is Not: 5 Steps to Get SPRS-Ready Before DIBCAC Shows Up

    CMMC Phase 2 Is Paused , Your Self-Assessment Is Not: 5 Steps to Get SPRS-Ready Before DIBCAC Shows Up

    Page: Cybersecurity and Defense Contracting
    Author: Penny Marbel, JPI Worldwide
    Revision date: September 17, 2026

    The Department of Defense has paused the universal rollout of CMMC Phase 2 third-party assessment requirements. Class Deviation 2026-O0025, Revision 3, effective September 3, 2026, moves the date for a universal CMMC mandate to November 10, 2028.

    The pause does not suspend the underlying cybersecurity obligations that apply to contractors and subcontractors handling Controlled Unclassified Information (CUI).

    For organizations subject to applicable contract requirements, DFARS 252.204-7012, NIST SP 800-171 Revision 2 controls, current Supplier Performance Risk System (SPRS) information, and cyber incident reporting obligations remain operational requirements. The government also retains authority to conduct independent Medium and High NIST assessments through the Defense Industrial Base Cybersecurity Assessment Center (DIBCAC) and related DoD assessment processes.

    Prime contractors may also impose cybersecurity, documentation, or certification requirements that are more restrictive than the minimum government contracting officer requirement.

    Quotable definition: A CMMC pause changes the timing and mechanism of certain assessments. It does not make CUI security, SPRS accuracy, or DFARS compliance optional.

    This article provides five practical steps for primes and subcontractors that need to prepare for a potential government assessment while reducing operational friction across the contractor team.

    Clean compliance workspace with a redacted System Security Plan and tabbed control families

    1. Confirm the Contractual Cybersecurity Baseline

    The first step is to identify which cybersecurity requirements apply to each contract, task order, subcontract, and information system.

    Do not rely only on the current CMMC phase schedule. Review the contract file and associated flow-down requirements for:

    • DFARS 252.204-7012, Safeguarding Covered Defense Information and Cyber Incident Reporting.
    • NIST SP 800-171 Revision 2 requirements.
    • DFARS 252.204-7021 or other CMMC language, where incorporated.
    • DFARS 252.240-7997 or other applicable NIST assessment requirements.
    • Prime contractor security addenda and subcontractor representations.
    • Cloud, remote-access, incident-reporting, and system-boundary requirements.
    • Requirements governing the handling of CUI by lower-tier subcontractors.

    The applicable system boundary must also be documented. A contractor should be able to identify which devices, users, applications, cloud services, locations, and support processes store, process, or transmit CUI.

    This is particularly important for subcontractors. A prime may require a specific system configuration, assessment record, evidence package, or annual affirmation even where the current government solicitation does not require a third-party certification.

    The official Class Deviation 2026-O0025 document should be reviewed with the operative contract language. The deviation does not replace contract-specific analysis.

    2. Reconcile the SSP, POA&M, and Actual Environment

    A System Security Plan (SSP) is not a historical narrative. It should describe the system as it exists during contract performance.

    Compare the SSP to the current environment and record discrepancies involving:

    • Network architecture.
    • User accounts and privileged access.
    • Multifactor authentication.
    • Endpoint protection and configuration management.
    • Logging, monitoring, and audit retention.
    • Media handling and removable storage.
    • Remote administration.
    • Cloud service providers.
    • Incident response responsibilities.
    • Physical and environmental safeguards.
    • Personnel termination and access-removal procedures.

    Each NIST SP 800-171 requirement should have a defensible implementation statement. The organization should be able to identify the responsible process owner, the supporting evidence, and any limitation or deficiency.

    A POA&M should not be used to conceal an unknown condition. It should identify the deficiency, risk, responsible party, milestone, resources, and expected completion date. The status of each item should be consistent with the score entered into SPRS.

    NIST describes SP 800-171 as a framework for protecting CUI in nonfederal systems and organizations. Its control families include access control, awareness and training, audit and accountability, configuration management, identification and authentication, media protection, personnel security, and system and communications protection. See the NIST SP 800-171 Revision 2 publication for the source requirements.

    3. Validate the SPRS Score and Annual Affirmation

    A SPRS score is an official representation of the contractor’s cybersecurity posture. It should not be treated as a one-time administrative entry.

    Before submitting or affirming a score, verify that:

    1. The score corresponds to the correct system security plan.
    2. The assessed system boundary is clearly defined.
    3. The applicable NIST version is correctly identified.
    4. The score reflects actual implementation status.
    5. Any POA&M items are accurately represented.
    6. The CAGE code and related system information are correct.
    7. The affirming official understands the basis for the representation.
    8. The annual affirmation is current.

    The organization should retain the calculation, supporting evidence, approvals, and change history used to establish the score. The records should be accessible to authorized personnel without disclosing CUI in unnecessary public or internal locations.

    A current score does not establish that every control is operating effectively at every moment. It does establish an accountable representation that should be supported by contemporaneous records.

    Where a material system change occurs, the contractor should determine whether the SSP, score, POA&M, or affirmation requires review or update. The same principle applies when a new subcontractor, cloud service, remote-access method, or technology platform enters the CUI environment.

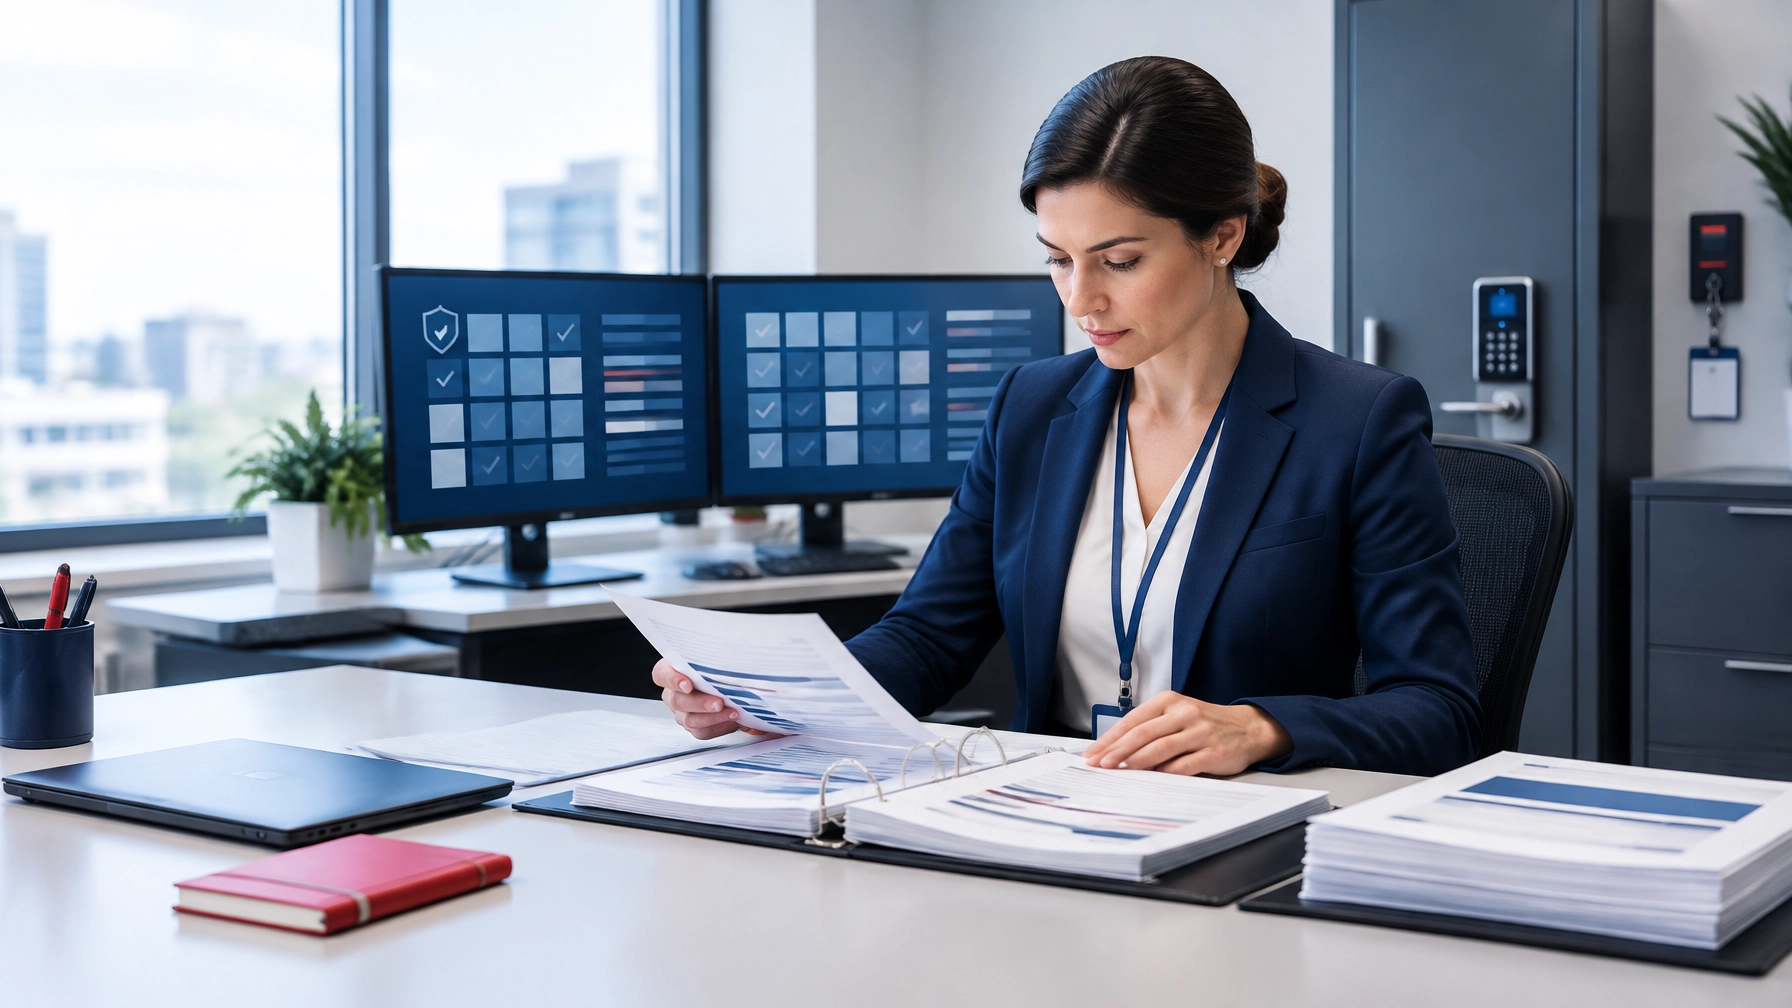
    Compliance team reviewing a dated risk register and an abstract SPRS readiness dashboard

    4. Build Evidence That an Assessor Can Verify

    An assessment is not satisfied by policy titles alone. Assessors may examine documents, interview personnel, review configurations, and seek demonstrations of how controls operate.

    Prepare an evidence index that maps each NIST requirement to objective evidence, such as:

    • Approved policies and procedures.
    • Access-control and account-review records.
    • Configuration baselines.
    • Vulnerability and patch reports.
    • Training records.
    • Incident response exercises.
    • Backup and recovery test results.
    • System-generated logs.
    • Change-management records.
    • Physical access reviews.
    • Supplier and cloud-service documentation.
    • Security assessment reports.
    • POA&M records and closure evidence.

    The evidence should be dated, attributable, and connected to the system described in the SSP. Screenshots without context may not demonstrate sustained implementation. Policies without records may not demonstrate execution.

    Personnel should also understand their responsibilities. An assessor may ask an administrator how privileged access is approved, an employee how incidents are reported, or a manager how overdue remediation is escalated.

    Training should therefore include controlled interviews. The purpose is not to script answers. The purpose is to ensure that personnel can accurately describe established procedures without disclosing information beyond the assessment scope.

    5. Prepare for Government and Prime Contractor Review

    DIBCAC or another authorized DoD assessment team may conduct a Medium or High NIST assessment independent of a contractor’s self-assessment. The assessment may include document review, discussions with personnel, verification of the SSP, and examination of how controls are implemented.

    The contractor should establish a formal assessment-readiness process that includes:

    • A designated assessment lead.
    • A controlled evidence repository.
    • A document request and response log.
    • A system-boundary diagram.
    • A current asset and account inventory.
    • A schedule for control-owner interviews.
    • A process for responding to findings.
    • Legal and contractual review of disclosures.
    • Coordination with the prime contractor where flow-down requirements apply.

    The organization should not provide more information than is required for the assessment. It should also avoid modifying records solely to improve appearance. Assessment records must remain accurate and traceable.

    The SPRS system and applicable DoD assessment procedures should be treated as part of the contractor’s continuing compliance process, not as a final administrative step.

    Prime contractors should apply the same discipline to subcontractor oversight. A prime may need evidence that a subcontractor has identified its CUI system, maintained an appropriate score, completed required affirmations, and reported incidents through the required chain of communication.

    What Does the CMMC Phase 2 Pause Mean for Contractors?

    The pause means that the universal Phase 2 requirement for third-party CMMC assessments is delayed. It does not remove existing contract obligations or prevent a program office, contracting officer, or prime contractor from imposing specific cybersecurity requirements where permitted.

    The universal CMMC mandate is now scheduled for November 10, 2028, subject to applicable future rulemaking and contract language. Until then, each contractor should review the requirements that apply to its specific contracts and systems.

    Does a Current SPRS Score Protect a Contractor From DIBCAC Review?

    No. A current SPRS score documents a self-assessment position. It does not prevent the government from conducting an independent Medium or High NIST assessment where authorized.

    The government may compare the score, SSP, POA&M, evidence, interviews, and observed implementation. A material inconsistency may create contractual, performance, or eligibility consequences.

    What Should a Subcontractor Do When a Prime Requires More Than the Government Clause?

    The subcontractor should obtain the requirement in writing, identify the affected information system, and confirm the required evidence, timing, and responsible party.

    Prime requirements may include additional security controls, specific reporting formats, independent reviews, or certification expectations. The subcontractor should not assume that the current CMMC pause invalidates those requirements.

    Practical Readiness Component: Five-Item SPRS and DIBCAC Checklist

    Before the next assessment request, confirm that the organization can answer “yes” to each question:

    • Is the applicable contract and subcontract cybersecurity language documented?
    • Does the SSP accurately describe the current CUI environment?
    • Does the SPRS score match the SSP, POA&M, and actual implementation status?
    • Can each control owner produce dated objective evidence?
    • Can the organization explain how it will respond to a government or prime contractor assessment?

    If any answer is “no,” the issue should be assigned, documented, and managed through a corrective-action process.

    JPI Worldwide supports government agencies, prime contractors, and subcontractors with cybersecurity architecture, secure network implementation, access-control design, system hardening, monitoring, technical staffing, and infrastructure integration. As a subcontractor, JPI can support defined technical work packages and help reduce operational friction between program, technical, and compliance teams. Review JPI cybersecurity capabilities, government support capabilities, or use the JPI contact page to discuss the requirements applicable to your business, agency, or department.

    This article is provided for informational purposes and does not constitute legal, contractual, or regulatory advice. Contractors should review their specific contract language and obtain qualified advice where applicable.
    Sources

  • IT Support in an Austere Theater: What First-Time Subcontractors Should Know Before They Deploy

    IT Support in an Austere Theater: What First-Time Subcontractors Should Know Before They Deploy

    Page: Field Operations Brief
    Revision date: September 17, 2026
    Author: Penny Marbel, JPI Worldwide

    For a company entering OCONUS work for the first time, “IT support services” may appear to be a standard technical requirement performed in a different country. In an austere theater, that assumption creates avoidable risk.

    An austere environment may lack dependable commercial power, transportation, warehouse access, replacement equipment, local technical labor, or continuous network connectivity. The work may also involve additional requirements for personnel screening, medical readiness, insurance, travel documentation, security training, and emergency planning.

    Quotable definition: An austere IT environment is an operating location where power, transportation, connectivity, facilities, personnel support, and replacement logistics cannot be assumed and must be planned as part of the technical solution.

    A first-time subcontractor does not need to perform every function internally. The company does need to understand the conditions, define its scope accurately, and identify where an experienced field-support partner can reduce operational friction for the prime contractor.

    1. Understand what “austere” means operationally

    Austere does not necessarily mean a combat zone. It means that ordinary business assumptions may not apply.

    The worksite may have limited or intermittent:

    • Electrical power and environmental control
    • Internet, voice, or other communications services
    • Roads, air transport, and local freight support
    • Secure storage and workspace
    • Technical labor and vendor support
    • Access to tools, consumables, and replacement parts
    • Medical, administrative, and emergency services

    The technical requirement may still be straightforward. The delivery conditions are not.

    The Department of Defense OCONUS Cloud Strategy recognizes the importance of bandwidth, power, deployable computing, edge processing, and technical personnel when systems operate outside conventional infrastructure. The same planning logic applies to network installation, help desk support, communications integration, and technology infrastructure more broadly.

    A first-time subcontractor should therefore ask a basic question before accepting the work:

    What must be supplied, protected, maintained, and replaced if the local environment cannot provide it?

    2. Distinguish garrison IT from field IT support

    Garrison IT support generally operates within established facilities and enterprise processes. The location may have structured cabling, stable power, approved network services, facilities personnel, local transportation, and nearby vendors.

    Field support may require the subcontractor to provide or coordinate more of the operating foundation. This can include:

    • Site preparation and equipment staging
    • Temporary or modular workspaces
    • Power conditioning, UPS equipment, or backup power interfaces
    • Local network installation and testing
    • Remote connectivity and communications integration
    • Environmental protection for equipment
    • Configuration documentation and as-built records
    • On-site troubleshooting and user training
    • Spare equipment and replacement procedures
    • Travel, access, rotation, and demobilization planning

    The distinction affects staffing, pricing, schedule, insurance, and risk allocation. A technician who is effective in a mature data center may require additional preparation before working independently at a remote site with limited support.

    A subcontractor should not describe a field assignment as “remote support” if the scope requires installation, physical troubleshooting, equipment movement, or independent operation at the site.

    3. Complete a site survey before committing to the design

    A site survey is not a formality. It is the basis for a credible deployment plan.

    Field technician documenting an unimproved site survey with a rugged tablet

    Where physical access is available, the survey should document the conditions that affect delivery and sustainment. Where access is not available, the subcontractor should identify assumptions, validation requirements, and contingency allowances.

    The survey should address:

    • Available power, voltage, outlets, grounding, and backup arrangements
    • Heat, dust, humidity, water exposure, and equipment ventilation
    • Existing racks, cabinets, pathways, cable routes, and workspace
    • Primary and secondary connectivity options
    • Required bandwidth, latency, and service availability
    • Physical access, storage, staging, and maintenance areas
    • Equipment dimensions, weight, environmental ratings, and mounting needs
    • Local restrictions affecting transport, installation, or communications
    • Required technical personnel and anticipated user population
    • Testing, cutover, rollback, and acceptance procedures

    The output should be usable by the prime contractor, government customer, installation team, and sustainment personnel. It should identify dependencies instead of hiding them.

    A site survey should not disclose sensitive location information in public documentation. Site records should be controlled according to the prime contract, customer direction, and applicable information-handling requirements.

    4. Plan spares and the logistics chain

    A field system is not supportable merely because the initial equipment arrives on site.

    Replacement logistics may involve long lead times, customs or host-country procedures, controlled access, limited transport windows, or a shipment that must pass through several coordination points. A first-time subcontractor should establish the replacement path before deployment.

    The plan should identify:

    • Failure-prone and mission-essential components
    • Recommended quantities of critical spares
    • Equipment serial-number and configuration records
    • Packaging, storage, and environmental protection requirements
    • Warranty and vendor escalation procedures
    • Authorized repair, replacement, and return processes
    • Resupply timelines and alternate transportation options
    • Responsibility for inventory, custody, and disposition
    • Procedures for secure media and failed equipment

    The objective is not to carry every possible replacement. The objective is to understand which failures stop the mission, which failures can be worked around, and how each category will be addressed.

    JPI’s capabilities include equipment staging, deployment coordination, network infrastructure, field installation, technical staffing, and sustainment support. An experienced subcontractor can help a new entrant convert a technical bill of materials into a field-ready deployment package.

    Compact equipment rack and operator workstation inside a climate-controlled container shelter

    5. Treat personnel readiness as a technical dependency

    Personnel readiness is part of the deployment plan. It is not an administrative item that can be resolved after the technical team is selected.

    Depending on the contract and operating location, personnel may need:

    • Valid passports, visas, entry permits, or transit documents
    • Background and security checks
    • Medical screening and required vaccinations
    • Personal security or theater-specific training
    • Country, area, or theater clearance
    • Emergency contact and next-of-kin records
    • Required licenses for vehicles or equipment
    • Appropriate insurance and evacuation provisions
    • Rotation, relief, and return-to-home-station plans

    FAR 52.225-19 addresses contractor personnel supporting designated operational areas or diplomatic or consular missions outside the United States. The clause includes requirements related to medical fitness, vaccinations, documentation, clearances, training, logistics, security, personnel data, and applicable laws. It also provides that the substance of the clause must be included in qualifying subcontracts.

    The specific contract controls. A subcontractor should review the prime contract, statement of work, flow-down clauses, site instructions, and insurance requirements before pricing or scheduling the deployment.

    Insurance also requires advance review. Depending on the contract, personnel status, location, and applicable law, the program may involve workers’ compensation, Defense Base Act considerations, medical evacuation, emergency evacuation, life insurance, travel coverage, or repatriation responsibilities. JPI provides a general overview in Defense Base Act Insurance, Explained. That information is not a substitute for advice from qualified insurance and legal professionals.

    6. Establish communication expectations with the stateside customer

    A deployed technician should not become the only person who knows the system status.

    Before departure, the subcontractor and prime should agree on:

    • The technical and contractual points of contact
    • Routine reporting frequency and format
    • Incident severity levels and response expectations
    • Approved remote-support methods
    • Change-control authority
    • Escalation paths for equipment, security, and logistics issues
    • Required documentation at installation and handoff
    • Conditions that require schedule or scope changes
    • The process for communicating degraded or unavailable services

    Reports should separate confirmed facts, working assumptions, risks, decisions needed, and actions assigned. This gives the prime contractor a reliable operating picture without requiring the field technician to make unauthorized commitments.

    A subcontractor should also confirm what information may be transmitted through ordinary email, ticketing tools, messaging platforms, or public forms. Classified information, Controlled Unclassified Information, export-controlled technical data, credentials, and sensitive site information should not be placed in an unsecured communication channel.

    7. Avoid the most common first-timer mistakes

    New OCONUS subcontractors frequently underestimate the non-technical work surrounding a technical deployment.

    The most common mistakes include:

    1. Assuming commercial infrastructure will be available.
      Power, connectivity, transportation, and local vendors may be limited or unavailable.

    2. Pricing the technician but not the deployment system.
      Travel, access, insurance, spares, staging, rotation, documentation, and sustainment may all affect cost.

    3. Sending personnel before validating readiness.
      Missing documents, training, medical requirements, or clearances can delay the deployment.

    4. Treating spares as an afterthought.
      A low-cost component may still create a long outage if replacement logistics are undefined.

    5. Failing to document assumptions.
      Unrecorded assumptions become disputes when site conditions differ from the proposal.

    6. Making the field technician responsible for program management.
      Technical staff should have a clear escalation structure and should not be expected to resolve contractual ambiguity independently.

    7. Working without an experienced field partner.
      A new entrant may have strong technical skills but limited experience with OCONUS movement, sustainment, personnel readiness, or prime-contractor coordination.

    8. Use a pre-deployment readiness review

    A formal readiness review should occur before personnel and equipment move.

    Austere deployment readiness checklist covering planning, spares, and personnel readiness

    At minimum, confirm:

    • Planning: Site conditions, power, connectivity, access, schedule, roles, and acceptance criteria
    • Spares: Failure priorities, inventory, replacement path, storage, and resupply
    • Personnel: Medical readiness, documentation, training, insurance, rotation, and emergency contacts
    • Security: Information-handling rules, physical access, reporting, and approved communications
    • Customer coordination: Points of contact, escalation procedures, change authority, and reporting cadence
    • Demobilization: Equipment recovery, configuration records, lessons learned, and continuing support

    The review should produce a documented go, no-go, or conditional-go decision. Open conditions should have an owner and resolution date.

    9. Identify where an experienced subcontractor fits

    A first-time subcontractor may contribute a specialized capability rather than a complete deployment enterprise. Possible niches include:

    • Network installation and troubleshooting
    • Structured cabling or wireless infrastructure
    • Help desk and user support
    • Communications equipment integration
    • Cybersecurity configuration and monitoring
    • Equipment staging and configuration management
    • Field service representation
    • Technical documentation and training
    • Logistics coordination and sustainment
    • Short-duration surge staffing

    The company should define what it can perform independently, what requires prime direction, and what should be assigned to an experienced partner.

    JPI Worldwide supports government agencies, prime contractors, and subcontractors with technology infrastructure, communications, cybersecurity, technical staffing, logistics, and field deployment services. JPI’s role can be structured around a defined technical package, a field-support assignment, or a broader deployment and sustainment requirement.

    Q&A: IT support services in austere OCONUS environments

    What is austere IT support?

    Austere IT support is the delivery and sustainment of technology systems where power, connectivity, transportation, facilities, personnel support, and replacement logistics are limited or uncertain.

    What should a first-time OCONUS subcontractor do first?

    The subcontractor should review the prime contract and flow-down requirements, define its scope, conduct or validate a site survey, confirm personnel readiness, and establish a spare-parts and escalation plan.

    Does the government provide all logistics and security support?

    Not necessarily. Contract terms control. FAR 52.225-19 states that, unless specified elsewhere in the contract, the contractor is responsible for logistical and security support required for covered contractor personnel.

    Why should a new entrant partner with an experienced subcontractor?

    An experienced subcontractor may reduce execution risk by providing established field processes, deployment personnel, logistics coordination, documentation practices, and communication with the prime. The arrangement should be defined in the subcontract and aligned with the prime’s performance requirements.

    How can JPI Worldwide help?

    JPI may support site planning, network and communications infrastructure, equipment staging, technical staffing, field installation, troubleshooting, logistics, and sustained operations in CONUS and OCONUS environments.

    Discuss the requirement with JPI Worldwide

    A new entrant does not need to manage every OCONUS requirement alone. The appropriate partner can help convert a technical capability into a deployable, supportable subcontracting package.

    Contact JPI Worldwide to discuss how JPI can support your business, agency, or department with IT support services, technology infrastructure, field personnel, communications, logistics, or deployment planning. Do not submit classified information, Controlled Unclassified Information, export-controlled technical data, passwords, credentials, or sensitive location details through the public contact form.


  • How to Keep AI Running When the Network Drops: 5 Steps for OCONUS Missions

    How to Keep AI Running When the Network Drops: 5 Steps for OCONUS Missions

    Page: JPI Worldwide Insights
    Revision date: September 17, 2026
    Author: Penny Marbel (JPI Worldwide)

    Artificial intelligence is increasingly expected to support operations outside conventional data-center conditions. In an OCONUS mission, connectivity may be intermittent, bandwidth may be limited, and reach-back to enterprise services may be unavailable for a defined period.

    An AI capability that depends on continuous cloud access may therefore become unavailable when it is most needed. The appropriate response is not to reproduce an entire enterprise environment at every field location. The appropriate response is to identify essential workloads, place selected processing at the edge, and establish controlled synchronization when connectivity returns.

    The Pentagon’s current AI strategy reflects this direction. The January 9, 2026 Artificial Intelligence Strategy for the Department of War calls for AI compute “from datacenters to the edge,” rapid model updates, modular architectures, and AI access across operational environments. These priorities are increasing demand for defense IT solutions that can function in classified, disconnected, denied, degraded, intermittent, or limited-connectivity conditions.

    Disconnected-first AI is an architecture in which defined AI functions continue locally during network outages, while data, models, and system status synchronize through controlled processes when connectivity is restored.

    The following five steps provide a practical framework for technical leads, prime contractors, government organizations, and potential integration partners.

    1. Define what must remain available locally

    A disconnected deployment must begin with an operational requirement, not a model selection.

    The technical team should identify which functions must continue when the network is unavailable. These functions may include:

    • Local equipment diagnostics.
    • Network and infrastructure monitoring.
    • Technical-document retrieval.
    • Maintenance or logistics triage.
    • Data classification and prioritization.
    • Cybersecurity event filtering.
    • Workflow routing and operator decision support.

    Each function should have a defined boundary. The system should specify what the AI may analyze, what it may recommend, and what requires human review or enterprise authorization.

    The requirement should also define the expected outage condition. A system designed for five minutes of intermittent connectivity may be materially different from a system that must operate for several days without reach-back.

    Technical leads should document:

    • Required local functions.
    • Authorized data sources.
    • Expected outage duration.
    • Maximum acceptable latency.
    • Human approval requirements.
    • Data retention and deletion rules.
    • Synchronization conditions.
    • Recovery and reconstitution procedures.

    A cloud service can remain part of the overall architecture. It should not be the only location where essential processing occurs.

    2. Build a low-SWaP edge-compute baseline

    Edge compute places processing and storage near the user, sensor, network, or operational system. In OCONUS environments, the equipment must also fit within practical constraints involving size, weight, and power, commonly referred to as SWaP.

    Low-SWaP edge computing means delivering the required local processing capability with the smallest practical equipment, weight, power demand, cooling burden, and sustainment requirement.

    Low-SWaP design does not mean selecting the smallest available device without regard to mission requirements. A compact platform that overheats, lacks storage, or cannot be maintained in the field may create more operational friction than a larger but properly engineered system.

    The baseline should address:

    • Processing requirements for local inference.
    • Storage capacity for queued data, logs, and approved reference material.
    • Power input, battery or generator limitations, and safe shutdown.
    • Thermal management and environmental protection.
    • Hardware replacement and spare-equipment planning.
    • Local network interfaces and segmentation.
    • Secure configuration and access controls.
    • Operator and maintainer skill requirements.

    Model selection should occur alongside hardware selection. A model that performs effectively in a centralized environment may require quantization, compression, pruning, or a different inference approach at the edge. The objective is to maintain an acceptable level of function without creating unnecessary hardware or power dependencies.

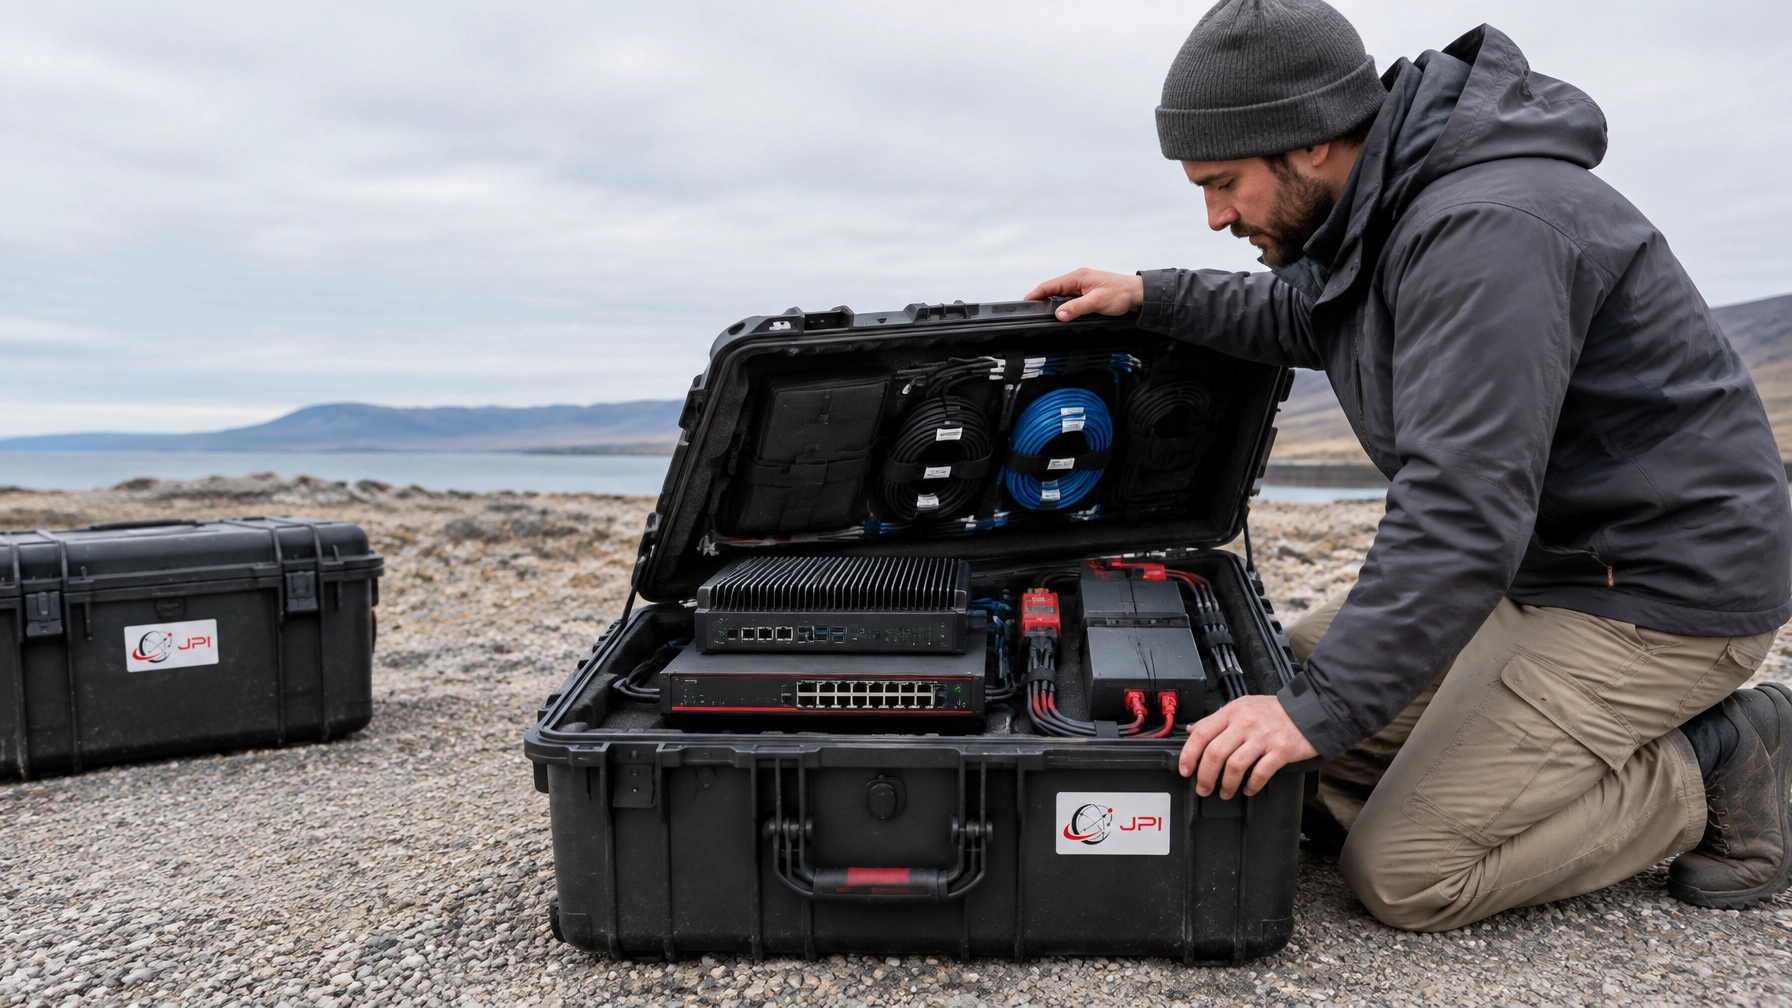
    Technician connecting a compact rugged compute module and network appliance inside an austere equipment shelter

    3. Use store-and-forward data flows

    A store-and-forward architecture allows an edge node to collect, process, and retain data locally until an approved connection becomes available. Once connectivity is restored, the system synchronizes selected information according to policy.

    The architecture should not automatically transmit every file, event, or model output. Data should be triaged before synchronization.

    A practical flow includes:

    1. Local collection: Gather data from approved systems, sensors, applications, or operator inputs.
    2. Local triage: Classify data by operational value, sensitivity, urgency, and transmission cost.
    3. Local inference: Apply approved AI functions and record the result with an audit trail.
    4. Connection detection: Identify when an authorized communications path is available.
    5. Policy-controlled synchronization: Transmit only approved records, logs, updates, or requests.
    6. Command-node validation: Review, accept, reject, or return information and configuration changes.

    The system should use queues with defined priorities. Critical system-health information may receive a higher priority than bulk telemetry. A summary or extracted feature may be transmitted before the original data set when policy permits.

    Synchronization should also support interruption. If a link fails during transfer, the system should preserve data integrity, record the transfer state, and resume or restart according to documented rules.

    Store-and-forward architecture showing data flow from a disconnected edge node to a command node after connectivity is restored

    4. Manage data, models, and updates over constrained links

    Model management becomes more difficult when the network cannot support large or frequent transfers. Updates must therefore be treated as controlled configuration changes rather than routine downloads.

    The technical baseline should maintain version records for:

    • AI models.
    • Model weights and supporting files.
    • Application containers.
    • Operating systems and dependencies.
    • Configuration files.
    • Data schemas.
    • Security policies.
    • Prompt, retrieval, or agent instructions.

    Each update should have an identified source, integrity verification, compatibility assessment, rollback path, and test record. The edge node should be able to continue operating on the last approved version if an update is incomplete or fails validation.

    The January 2026 Department of War AI strategy directs the establishment of a delivery and integration cadence intended to support rapid model updates. In a constrained OCONUS environment, that objective requires more than a fast release schedule. It requires a transport and sustainment process that can function when links are intermittent.

    Practical methods may include:

    • Shipping approved updates through controlled physical media where permitted.
    • Transmitting only changed components rather than full packages.
    • Compressing models and supporting data.
    • Scheduling updates during defined synchronization windows.
    • Maintaining multiple approved model versions.
    • Separating urgent security patches from optional capability updates.
    • Testing updates on a representative edge platform before deployment.
    • Recording update status locally until confirmation is received.

    Model updates should not be treated as automatically beneficial. Performance, resource consumption, data compatibility, and security implications should be evaluated before the update is released to an operational node.

    5. Design for graceful degradation

    Graceful degradation means that a system reduces capability in a controlled manner rather than failing unpredictably when a dependency is unavailable.

    An AI system may operate through several defined modes:

    • Connected mode: Full authorized integration with enterprise services.
    • Constrained mode: Reduced bandwidth, delayed synchronization, or limited external services.
    • Disconnected mode: Local inference, local data access, and local audit logging.
    • Recovery mode: Controlled synchronization, validation, reconciliation, and service restoration.

    Each mode should have known limitations. Operators should be able to see whether the system is connected, what data is current, which services are unavailable, and when the last successful synchronization occurred.

    The system should also establish safeguards for stale or incomplete data. AI outputs based on old records may require a different confidence designation or additional human review. If required data is unavailable, the system should state that limitation rather than implying that the result is complete.

    Graceful degradation should include:

    • Local status displays.
    • Clear alerts for stale data.
    • Manual override and disengagement procedures.
    • Local audit logs during outages.
    • Recovery testing after link restoration.
    • Data reconciliation procedures.
    • Defined escalation routes.
    • Training for operators and maintainers.

    Operator reviewing local system status inside a compact equipment shelter with edge-compute hardware and organized cable runs

    Q&A: AI for disconnected OCONUS missions

    What is the main advantage of edge AI in a disconnected environment?

    The principal advantage is local availability of defined AI functions when continuous access to a centralized cloud or enterprise network cannot be assumed. Edge AI does not eliminate the need for centralized systems. It provides a controlled local capability for selected workloads.

    Is store-and-forward the same as real-time connectivity?

    No. Store-and-forward systems are designed for delayed or intermittent exchange. They collect and process data locally, then synchronize selected information when an approved connection is available.

    What does low-SWaP mean for defense IT solutions?

    Low-SWaP refers to reducing the size, weight, and power requirements of the deployed technology while preserving the processing, storage, security, and environmental capabilities required by the mission.

    How should AI model updates be handled in disconnected environments?

    Updates should be version-controlled, integrity-checked, tested, documented, and capable of rollback. The system should continue operating on the last approved version if a new update is incomplete, incompatible, or not authorized.

    What should primes require from an edge AI subcontractor?

    Primes should require documented interfaces, defined degraded-mode behavior, cybersecurity controls, data and model governance, test evidence, human-oversight procedures, configuration management, field support, and sustainment responsibilities. A successful demonstration alone does not establish deployment readiness.

    How JPI Worldwide can support implementation

    JPI Worldwide supports AI and systems integration, network engineering, cybersecurity, communications, technical staffing, logistics, and field deployment. These capabilities can be combined to reduce integration friction for primes and government organizations implementing edge AI in CONUS and OCONUS environments.

    JPI may support:

    • Edge-compute and network architecture planning.
    • Store-and-forward communications and synchronization design.
    • AI-enabled workflow and systems integration.
    • Network segmentation, secure access, and monitoring.
    • Hardware staging, configuration, and field installation.
    • Operational testing and troubleshooting.
    • Technical staffing for deployment and sustainment.
    • Training, documentation, and system handoff.
    • Equipment movement and deployment coordination.

    JPI’s government support capabilities are structured for requirements that extend beyond software delivery. Infrastructure, personnel, logistics, cybersecurity, and sustainment may all affect whether an AI capability remains useful after deployment.

    Contact JPI Worldwide

    Potential partners, technical leads, prime contractors, government agencies, and departments evaluating network deployment services or defense IT solutions may contact JPI Worldwide to discuss a requirement.

    Do not submit classified information, Controlled Unclassified Information, export-controlled technical data, passwords, credentials, or other sensitive material through the public contact form. Contact JPI directly if the requirement requires a secure communications method.

    Sources and further reading

  • Wet Tees and Desert Heat: 5 Lessons from the Army’s Starlink Trial for Tactical Communications Planners

    Wet Tees and Desert Heat: 5 Lessons from the Army’s Starlink Trial for Tactical Communications Planners

    Page: Technology Infrastructure and Mission Support
    Revision date: September 17, 2026
    Author: Penny Marbel (JPI Worldwide)

    During the Army’s Project Convergence Capstone 6 exercise in July 2026, some commercial Starlink ground terminals experienced overheating in more than 100-degree desert heat. The elevated temperatures reduced data throughput. Soldiers responded by soaking T-shirts in water and placing them over the terminals to provide evaporative cooling and shade.

    The event was not merely an anecdote about field improvisation. It was a practical demonstration of the engineering and acquisition decisions that affect tactical communications and telecom infrastructure in demanding environments.

    Commercial technology may provide speed, availability, and lower acquisition cost. Ruggedized equipment may provide greater environmental margin. Neither category is automatically appropriate for every mission. The relevant question is whether the complete system, operating procedure, and sustainment model are suitable for the conditions in which the government expects the capability to function.

    Quotable definition: Thermal management is the planned control of heat entering, accumulating within, and leaving a system so that the system remains within its operating limits.

    The following five lessons are intended for government buyers, contracting officers, program managers, and prime contractors evaluating communications capabilities for field use.

    1. Test the Environment, Not Only the Equipment

    A technology evaluation should reproduce the environmental conditions that may affect mission performance. Laboratory specifications and manufacturer data are necessary, but they may not capture the combined effect of direct solar loading, reflected heat, dust, restricted airflow, vehicle exhaust, power-conversion losses, and continuous operating cycles.

    The Starlink trial illustrated how a system that performs adequately in ordinary commercial conditions may encounter limitations when placed in direct sun and extreme heat. Throughput degradation may be operationally significant even when the equipment does not immediately fail.

    For a government buyer, the solicitation and evaluation plan should identify applicable environmental conditions, including:

    • Ambient temperature and solar exposure
    • Dust, sand, humidity, precipitation, and wind
    • Vehicle-mounted or enclosed operating conditions
    • Available power and power-quality limitations
    • Expected duty cycle and peak traffic demand
    • Required data rates during degraded conditions
    • Maintenance access and replacement procedures

    Environmental testing should also examine system performance rather than equipment survival alone. A terminal that remains powered on but reduces throughput below the mission requirement may not satisfy the intended operational need.

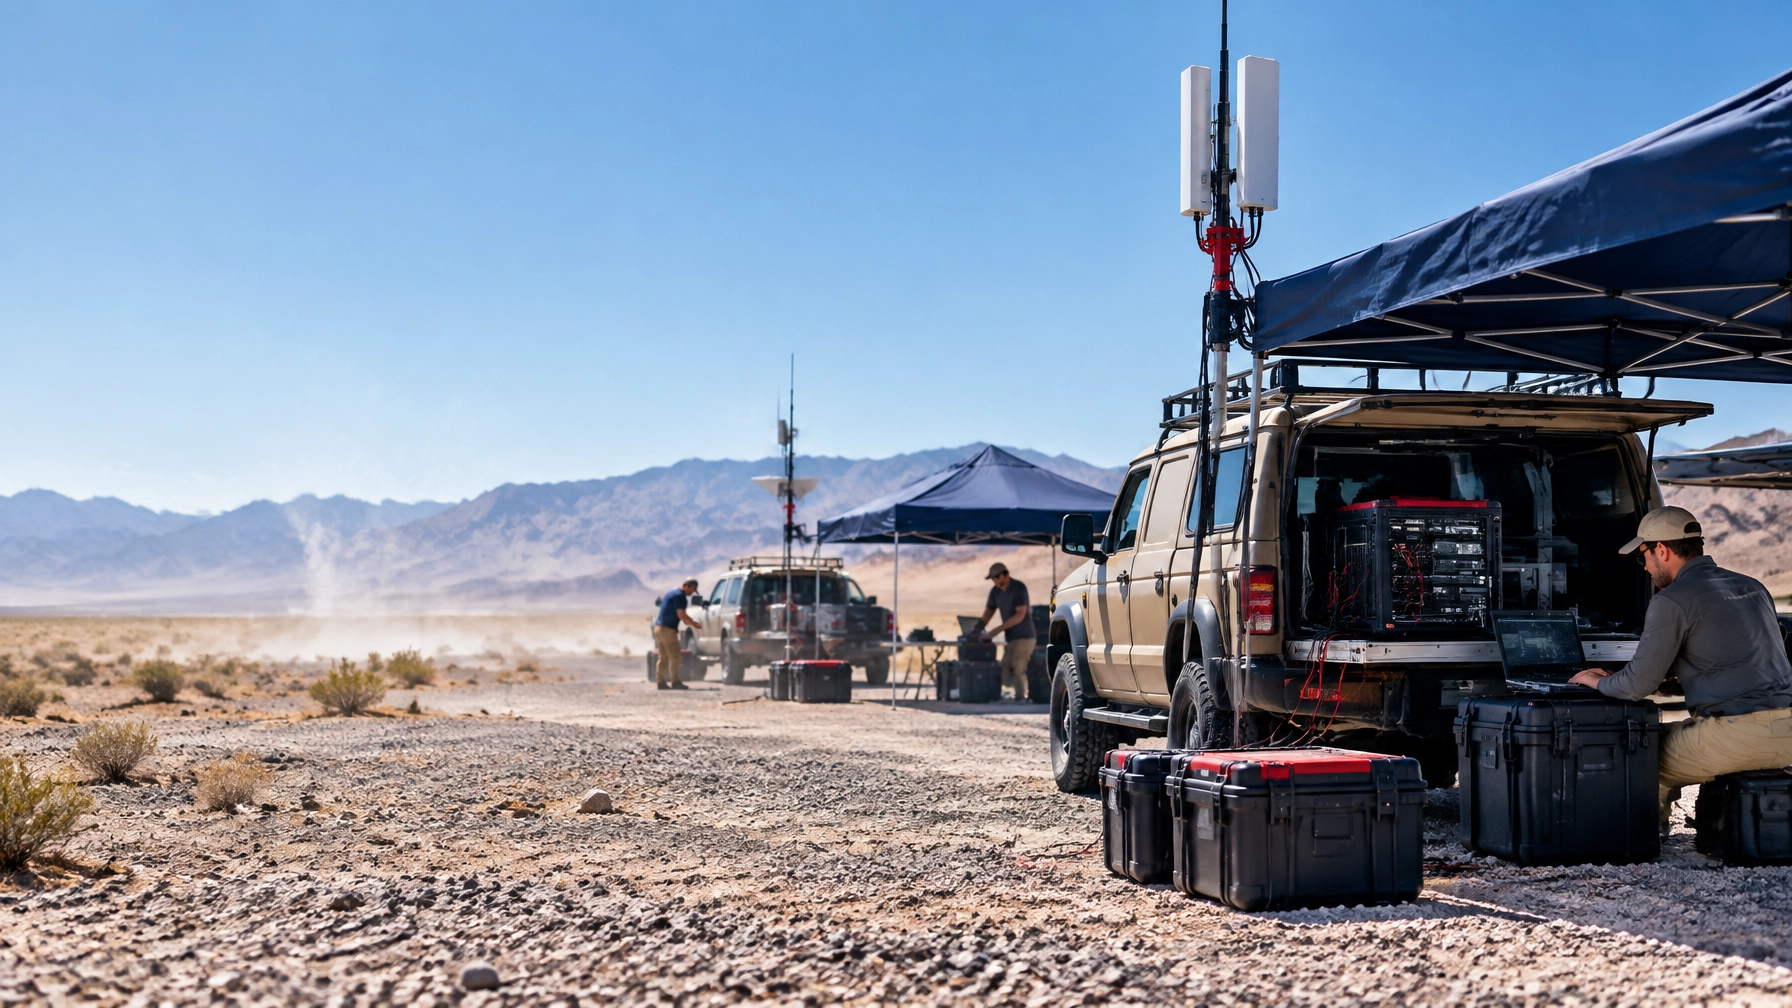
    Close-up of dust-affected communications equipment, shade material, thermal barriers, and field cabling in a desert environment

    2. Treat Thermal Management as Part of the Architecture

    Thermal management should be addressed during system design. It should not be treated as an afterthought assigned to field personnel after deployment.

    Possible design measures may include:

    • Shade structures that do not obstruct required signal paths
    • Reflective barriers or coatings
    • Ventilated equipment enclosures
    • Active cooling or vehicle-integrated cooling systems
    • Temperature sensors and threshold alerts
    • Equipment spacing that preserves airflow
    • Power systems sized to avoid unnecessary heat generation
    • Preventive cleaning and inspection procedures

    The Army’s reported consideration of additional cooling solutions, including vehicle-integrated systems, reflects a broader architectural principle. A terminal may be only one component of a larger communications package. The vehicle platform, power distribution, enclosure, network equipment, and environmental controls may determine whether the terminal can remain useful under operational conditions.

    A contracting officer should therefore avoid specifying a communications terminal without defining the surrounding integration requirements. The statement of work should identify who is responsible for mounting, cooling, power, cable routing, environmental protection, monitoring, and corrective maintenance.

    Field technician in a red JPI Worldwide polo using a thermal camera to inspect communications equipment mounted on a vehicle platform

    3. Document Field Expedients Without Making Them the Primary Control

    The wet-T-shirt solution demonstrated practical field ingenuity. It also showed why field expedients should be documented, evaluated, and incorporated into training when they are safe and operationally appropriate.

    A field expedient is a temporary or improvised method used to maintain or restore system function when the planned configuration is insufficient or unavailable. It may be useful when:

    • The method does not create an electrical, safety, or contamination hazard.
    • The method does not interfere with signal performance or equipment operation.
    • Personnel can apply the method consistently.
    • Required materials are available in the operating environment.
    • The method has been tested or approved through an appropriate technical process.
    • The method does not conceal a recurring design deficiency.

    The existence of a simple workaround does not establish that a system is ready for broad deployment. A wet cloth may provide short-term cooling under particular conditions. It may not be appropriate for prolonged operation, freezing conditions, sensitive electrical interfaces, water-constrained environments, or systems requiring unattended service.

    Government buyers should require a clear distinction between:

    1. Designed capability, which is part of the approved system configuration.
    2. Approved operating procedure, which is trained and documented.
    3. Emergency field expedient, which may be used only under defined conditions.
    4. Corrective engineering action, which addresses a recurring or unacceptable limitation.

    This distinction protects both mission performance and contract accountability.

    4. Buy for the Mission, Not for a Category Label

    “Commercial” and “ruggedized” are useful descriptors, but they do not replace requirements analysis. Commercial technology may be faster to procure, easier to update, and less expensive than a bespoke military system. Ruggedized equipment may offer greater environmental tolerance, but it may also increase cost, lead time, weight, power demand, and maintenance complexity.

    The Army’s experience supports a risk-based approach. A government customer should determine where additional ruggedization is necessary and where a commercial solution, protective integration, or documented operating procedure may provide sufficient value.

    Qualitative comparison of commercial COTS, ruggedized equipment, and integrated mission architecture for government telecom infrastructure

    The graphic above is a conceptual procurement aid. It is not a product specification, test result, or formal rating of any particular system.

    The acquisition analysis should consider:

    • Consequences of degraded throughput
    • Required availability and restoration time
    • Environmental exposure and deployment duration
    • Cost of replacement equipment and field labor
    • Availability of spare parts and technical support
    • Weight, power, and transportation constraints
    • Cybersecurity and network-integration requirements
    • Whether the system will operate attended or unattended
    • The cost of over-ruggedizing equipment that could be protected through integration

    A commercial-first strategy can reduce cost and accelerate fielding. It does not eliminate the need for environmental testing, integration engineering, or sustainment planning.

    5. Sustain the Whole System

    Tactical communications reliability depends on more than the terminal or radio. It depends on the complete telecom infrastructure package and the personnel responsible for operating it.

    A sustainment plan should address:

    • Configuration control and technical documentation
    • Operator and maintainer training
    • Environmental inspection criteria
    • Temperature and throughput monitoring
    • Spare equipment and replacement components
    • Troubleshooting and escalation procedures
    • Cooling, shade, power, and enclosure requirements
    • Network failover and alternate communications paths
    • Equipment movement and resupply
    • Corrective-action reporting and lessons learned

    Prime contractors should also define subcontractor responsibilities before deployment. Unclear interfaces between the equipment vendor, network integrator, field technician, logistics provider, and government customer can increase operational friction.

    JPI Worldwide supports primes and government customers with network engineering and infrastructure, satellite and communications integration, cybersecurity, technical staffing, logistics, field installation, troubleshooting, and sustained operational support. These capabilities may be combined into a defined subcontract work package covering design, staging, deployment, testing, and sustainment.

    JPI Deployment Component

    JPI may support a prime contractor or government program by providing the technical component required to move a communications capability from procurement to field operation. Depending on the requirement, that component may include:

    • Environmental and site-readiness assessments
    • Vehicle or facility integration
    • Network and power coordination
    • Equipment staging and configuration
    • Field installation and acceptance testing
    • Thermal monitoring and maintenance procedures
    • Operator training and technical documentation
    • Spare-parts and replacement planning
    • CONUS and OCONUS field support

    The final scope should be established by the statement of work, system architecture, security requirements, operating environment, and applicable law.

    Five practical lessons for tactical communications planners: test the environment, plan thermal management, define field expedients, buy for the mission, and sustain the whole system

    Frequently Asked Questions

    What happened to the Starlink terminals during Project Convergence Capstone 6?

    During the July 2026 exercise, some commercial ground terminals overheated in extreme desert heat. The resulting thermal throttling reduced data throughput. Soldiers used water-soaked T-shirts as an improvised cooling measure.

    Does the incident mean commercial technology is unsuitable for government missions?

    No. It demonstrates that commercial technology must be evaluated against the actual environmental and operational requirements. Commercial equipment may be suitable when it is properly integrated, protected, monitored, and supported.

    Is ruggedized equipment always the better procurement choice?

    No. Ruggedization may increase cost, weight, power consumption, and lead time. The appropriate choice depends on mission consequence, environmental exposure, availability requirements, and the effectiveness of alternative controls.

    What should a contracting officer include in a tactical communications requirement?

    The requirement should address environmental conditions, throughput under degradation, thermal management, power, mounting, cybersecurity, network integration, testing, training, spares, field support, and corrective-action procedures.

    How can JPI support a tactical communications program?

    JPI may provide communications integration, network infrastructure, cybersecurity, technical personnel, logistics, field deployment, troubleshooting, and sustainment support. Government and prime-contractor support capabilities are described here.

    Contact JPI Worldwide

    Government agencies, contracting officers, prime contractors, and mission partners evaluating tactical communications or broader telecom infrastructure may contact JPI Worldwide to discuss the technical and operational requirement.

    JPI can review:

    • Commercial and ruggedized equipment tradeoffs
    • Thermal management and environmental testing
    • Vehicle, facility, and field integration
    • Network architecture and secure access
    • Redundant communications paths
    • Technical staffing and field services
    • Logistics, spares, and sustainment

    Use the JPI Worldwide contact page or email connect@jpiworldwide.com. Do not submit classified information, Controlled Unclassified Information, export-controlled technical data, passwords, credentials, or other sensitive information through a public contact channel.

    Sources

    1. Breaking Defense: Wet Tees on Sat Links: Army’s Desert Trial Reveals Commercial Tech Challenges and Opportunities
    2. Breaking Defense: Project Convergence to Stress-Test Next-Gen Communications Gear in Sweltering Desert
    3. JPI Worldwide: Integrated Technology Capabilities
    4. JPI Worldwide: Government Technology and Mission Support

  • DoDNet Is Coming: What Defense IT Contractors Should Know Before Bidding on Network Migration Work

    DoDNet Is Coming: What Defense IT Contractors Should Know Before Bidding on Network Migration Work

    Page: Government Technology and Infrastructure
    Revision date: September 17, 2026
    Author: Penny Marbel, JPI Worldwide

    The Department of Defense is moving toward a standardized network architecture for all 11 combatant commands. The effort is expected to affect approximately 231,000 users across roughly 200 global sites and is targeted for completion by the end of fiscal year 2028.

    For defense IT contractors, the opportunity is significant. The schedule is also compressed. Contractors preparing to participate as primes, subcontractors, or specialized teaming partners should begin organizing technical evidence, migration resources, past performance, and execution controls before a formal solicitation is released.

    Quotable definition: DoDNet migration is the planned transition of combatant command common-use network services from separate NIPRNet and SIPRNet environments into a standardized, DISA-managed service-provider model, subject to applicable security and mission requirements.

    1. What is changing?

    The May 2026 Department of Defense Chief Information Officer directive instructed the Defense Information Systems Agency to migrate combatant command common-use unclassified and classified services to the DoDNet architecture by the end of FY2028.

    The effort is intended to reduce the operational and technical burden created by separate network environments. Public reporting describes the related market research effort as a CommandNet migration to DoDNet. The terms may appear together in acquisition documents and industry communications.

    The planned scope includes:

    • All 11 combatant commands.
    • Approximately 231,000 users.
    • Approximately 200 global sites.
    • Both NIPRNet and SIPRNet service environments.
    • Network discovery, transition planning, migration execution, and sustainment.
    • Identity, credential, and access management.
    • Zero-trust security capabilities.
    • Infrastructure-as-code and automated deployment methods.
    • Migration runbooks and risk-mitigated milestone schedules.

    The planned consolidation does not mean that classification boundaries may be disregarded. Contractors must understand the distinction between a standardized service model and the specific technical, security, access, and authorization requirements that apply to each environment.

    Conceptual network-consolidation diagram showing separate NIPRNet and SIPRNet environments transitioning to a standardized DoDNet service model

    2. Why is the acquisition approach changing?

    DISA previously considered expanding an existing enterprise contract without a new competition. That approach was challenged through the bid protest process. Following corrective action, DISA began new market research to reassess the acquisition strategy and obtain industry feedback.

    The change is material for contractors that previously viewed the opportunity as inaccessible. New market research may create openings for:

    • A potential prime contractor with enterprise migration capability.
    • A systems integrator with strong zero-trust and identity-management experience.
    • A network infrastructure contractor with distributed deployment resources.
    • A specialized subcontractor supporting site surveys, fiber, configuration, testing, or cutover.
    • A technical staffing provider able to support multiple locations and workstreams.
    • A logistics and field-services partner able to coordinate equipment and personnel movement.

    The acquisition approach remains subject to change. A sources-sought notice or request for information does not constitute a promise of a solicitation, award, contract type, or funding level. Contractors should treat the notice as a requirement signal and prepare evidence that can be used in later capture, teaming, and proposal activities.

    The publicly reported DISA market research notice requested information regarding technical approaches, transition plans, cost estimates, and relevant past performance. The SAM.gov opportunity record should remain the controlling source for official notice language and amendments.

    3. What does the 220-day procurement cycle mean?

    DISA has indicated that the anticipated competitive procurement cycle may be approximately 220 days from solicitation release to contract award.

    That period may appear substantial. It is not substantial when measured against the technical scope and the September 30, 2028 target. The winning team may need to complete discovery, planning, staffing, site coordination, engineering, migration, testing, and operational handoff within a limited execution window.

    A contractor should therefore prepare before the solicitation is issued.

    The 220-day period may include:

    1. Solicitation review and requirements decomposition.
    2. Questions, amendments, and proposal development.
    3. Team formation and responsibility allocation.
    4. Technical solution development.
    5. Staffing and labor-category validation.
    6. Past-performance and experience mapping.
    7. Cost and price development.
    8. Security, facility, and clearance planning.
    9. Proposal submission, evaluation, discussions, and award.

    A contractor that waits until solicitation release to identify technical partners may have limited time to conduct meaningful due diligence. Primes should establish a controlled teaming process. First-time subcontractors should prepare concise capability evidence that can be evaluated without extensive reconstruction.

    Fiber technician terminating strands at an enterprise patch panel

    4. What should primes prepare before bidding?

    Primes should prepare a migration operating model rather than a list of disconnected capabilities. The government will likely need evidence that a proposed team can manage technical dependencies, schedule risk, user impact, and operational continuity at scale.

    A bid-readiness review should address at least the following areas.

    Technical architecture

    The team should document its approach to:

    • Network discovery and dependency mapping.
    • Segmentation and boundary management.
    • Identity, credential, and access management.
    • Zero-trust implementation.
    • Configuration management.
    • Infrastructure as code.
    • Monitoring, logging, and operational visibility.
    • Testing, validation, and rollback.
    • Legacy-system integration.
    • Sustainment after cutover.

    Migration execution

    The proposed approach should explain how the team will:

    • Establish a repeatable site-migration method.
    • Sequence work across multiple locations.
    • Validate readiness before each cutover.
    • Manage user, application, and service dependencies.
    • Maintain change control.
    • Record configuration baselines.
    • Escalate unresolved technical issues.
    • Conduct post-migration verification.
    • Transfer knowledge to the responsible operations organization.

    Schedule control

    The team should show how it will build a realistic schedule that accounts for:

    • Site surveys and data collection.
    • Equipment availability.
    • Personnel access and travel requirements.
    • Network and application dependencies.
    • Testing windows.
    • Approval gates.
    • Rework and remediation.
    • Parallel workstreams.
    • Operational constraints.

    A schedule that shows only installation dates is incomplete. A credible schedule must show discovery, decision points, acceptance criteria, and contingency paths.

    5. What should first-time subcontractors demonstrate?

    First-time subcontractors should not attempt to compete with a prime on every capability. A stronger approach is to define a specific contribution that reduces execution risk.

    Useful evidence may include:

    • Fiber and structured cabling installation.
    • Routing, switching, and wireless infrastructure.
    • Network operations support.
    • Site surveys and technical assessments.
    • Configuration and commissioning.
    • Test planning and verification.
    • Field troubleshooting.
    • Technical documentation and runbook development.
    • Secure access implementation.
    • Staffing for distributed deployment teams.
    • Equipment staging and deployment logistics.
    • CONUS and OCONUS field support.

    Subcontractors should map each claimed capability to a deliverable, labor category, certification, past-performance example, or measurable result where disclosure is permitted.

    A capability statement should also identify limitations. For example, a subcontractor should state whether it provides design authority, installation support, testing support, or sustainment personnel. Precision reduces ambiguity during teaming discussions and proposal execution.

    6. How can contractors reduce operational friction?

    Network migration programs generate friction when responsibilities are unclear. Primes should seek subcontractors that can integrate into established processes without creating separate administrative systems for every task.

    Operationally useful subcontractors generally provide:

    • Clear points of contact.
    • Defined work packages.
    • Consistent technical documentation.
    • Reliable status reporting.
    • Controlled change management.
    • Personnel who can work within prime-contractor procedures.
    • Early identification of schedule or access constraints.
    • Practical field support after design approval.
    • Coordination between technical, logistics, and program teams.

    JPI Worldwide supports prime contractors and government customers with network engineering, infrastructure deployment, cybersecurity integration, technical staffing, logistics, and field services. Its capabilities include fiber and structured network infrastructure, routing and switching, wireless connectivity, secure access, monitoring, installation, testing, troubleshooting, and sustained technical operations.

    The JPI Worldwide capabilities page provides additional information about network engineering, cybersecurity, technical staffing, logistics, and systems integration. The government support page describes how JPI participates in government programs and larger contractor teams.

    Engineer inspecting equipment in a modern enterprise data center aisle

    7. What should contractors do now?

    A contractor preparing for DoDNet-related work should complete the following actions:

    1. Review the public requirement. Separate stated requirements from assumptions and identify areas requiring official clarification.
    2. Build a capability matrix. Map technical requirements to internal resources, partners, evidence, and gaps.
    3. Identify teaming needs. Determine whether the program requires field installation, identity management, cybersecurity, staffing, logistics, or sustainment partners.
    4. Prepare migration evidence. Organize examples of discovery, transition, testing, cutover, remediation, and operational handoff.
    5. Validate personnel availability. Confirm labor categories, geographic flexibility, credentials, technical qualifications, and mobilization timelines.
    6. Develop a risk register. Address access, equipment, dependencies, schedule compression, configuration control, and operational continuity.
    7. Protect sensitive information. Do not place classified information, CUI, credentials, security details, or controlled technical data in public inquiries or unsecured capability materials.
    8. Monitor official updates. Requirements, acquisition strategy, schedule, and contract structure may change.

    Timeline from the May 2026 directive through the approximately 220-day procurement cycle to the FY2028 target

    8. Frequently asked questions

    What is the DoDNet migration opportunity?

    It is a planned enterprise network migration affecting all 11 combatant commands, approximately 231,000 users, and roughly 200 global sites. The effort is targeted for completion by the end of FY2028.

    Is the work limited to network installation?

    No. Publicly reported requirements include discovery, transition planning, zero-trust architecture, identity and access management, infrastructure as code, migration methodologies, testing, and sustainment.

    Can a first-time subcontractor participate?

    A first-time subcontractor may participate where it provides a defined capability that supports the prime’s delivery model. Relevant evidence, personnel availability, technical scope, and execution controls will be important.

    Is the acquisition strategy final?

    No. DISA is conducting market research after corrective action related to an earlier acquisition approach. Contractors should rely on official notices and amendments for controlling requirements.

    What is the expected procurement timeline?

    DISA has indicated an anticipated competitive procurement cycle of approximately 220 days from solicitation release to award. The timing may change based on acquisition decisions and applicable procurement requirements.

    9. Contact JPI Worldwide

    JPI Worldwide can help prime contractors and government teams assess network infrastructure, field deployment, technical staffing, cybersecurity integration, logistics, and sustainment requirements related to complex migration programs.

    To discuss how JPI may support your business, agency, or department, use the JPI Worldwide contact page, email connect@jpiworldwide.com, or call +1-509-210-3023.

    Do not submit classified information, CUI, export-controlled technical data, passwords, credentials, or other sensitive material through the public contact form.

    Sources

  • CMMC Phase 2 Is Paused. Your Cybersecurity Obligations Are Not: 7 Steps for Government Contractors Right Now

    CMMC Phase 2 Is Paused. Your Cybersecurity Obligations Are Not: 7 Steps for Government Contractors Right Now

    Page: Government Contracting Insights
    Revision date: September 17, 2026
    Author: Penny Marbel, JPI Worldwide

    The Department of Defense issued DARS Class Deviation 2026-O0025, Revision 3, on September 3, 2026. The revision codifies the suspension of CMMC Phase 2 third-party assessment requirements.

    Under the revised direction, contracting officers must remove suspended requirements from active solicitations and modify existing contracts at the next option period or administrative update, as applicable.

    The pause does not eliminate the underlying cybersecurity obligations for government contractors handling Controlled Unclassified Information (CUI). Contractors must continue to address applicable requirements under DFARS 252.204-7012, maintain the NIST SP 800-171 Revision 2 baseline where required, complete self-assessments, maintain supporting records, and accurately report their status.

    Quotable definition: A CMMC Phase 2 pause changes how certain cybersecurity requirements may be assessed. It does not suspend the obligation to safeguard covered defense information or accurately represent the contractor’s cybersecurity posture.

    The following seven steps provide a practical response for primes and subcontractors that handle CUI.

    1. Confirm which contract requirements apply

    Contractors must begin with the actual contract, solicitation, and applicable flow-down provisions.

    A CMMC requirement may be removed or revised from an active solicitation. An existing contract may be modified at the next option exercise or administrative update. However, the contract language currently in force remains the controlling reference until a formal modification is executed.

    Review:

    • DFARS 252.204-7012, “Safeguarding Covered Defense Information and Cyber Incident Reporting.”
    • Any applicable DFARS assessment, scoring, or affirmation requirements.
    • CMMC language in solicitations, awards, task orders, and modifications.
    • Prime contract provisions that must be flowed down to subcontractors.
    • The definition and location of CUI or covered defense information.
    • Any contract-specific cybersecurity, incident reporting, or operationally critical support obligations.

    The pause should not be treated as permission to stop performing a contract requirement. Contracting officers, legal counsel, and the prime contractor should be consulted where the requirement is unclear.

    The DARS Class Deviation 2026-O0025 resource provides a public summary of the revision. Contractors should verify requirements against the applicable contract and official DoD guidance.

    2. Define the CUI environment and system boundary

    Cybersecurity obligations cannot be assessed accurately until the organization knows which systems, users, applications, facilities, and service providers are within scope.

    A contractor should document:

    • Where CUI is received, stored, processed, or transmitted.
    • Which endpoints and servers can access CUI.
    • Which cloud services or managed service providers support the environment.
    • Which users, administrators, and subcontractors require access.
    • Which network segments are included or excluded.
    • How data enters and leaves the controlled environment.
    • Which systems support contract performance but do not process CUI.

    Locked network cabinet with disciplined patch panels and cable management

    A poorly defined boundary can create two separate risks. The organization may assess too small an environment and omit systems that require protection. Alternatively, it may include unnecessary systems and create avoidable cost and administrative burden.

    For primes, the boundary review should include subcontractor interfaces and shared technology. For subcontractors, the review should identify whether CUI is being accessed through a prime-controlled environment, a subcontractor-controlled system, or a third-party service.

    3. Perform an evidence-based NIST SP 800-171 assessment

    The CMMC Phase 2 pause does not remove the need to assess the applicable NIST SP 800-171 Revision 2 requirements.

    The assessment should address all applicable requirements and should be supported by objective evidence. A policy statement alone may not demonstrate implementation.

    Useful evidence may include:

    • Approved policies and procedures.
    • System Security Plans.
    • Configuration records.
    • Access-control and authentication records.
    • Security awareness and training records.
    • Vulnerability management reports.
    • Incident response procedures and test results.
    • Backup and recovery records.
    • Media protection and sanitization records.
    • Asset inventories and network diagrams.
    • Physical access records.
    • Supplier and managed-service documentation.

    Each requirement should have a clear status. The organization should distinguish between:

    • Implemented controls.
    • Partially implemented controls.
    • Planned controls.
    • Controls that are not applicable, with a documented rationale where permitted.

    A self-assessment should reflect the implemented state, not the desired future state. Inflating a score to improve proposal positioning can create material legal and contractual risk.

    4. Maintain the SSP, POA&M, SPRS score, and annual affirmation

    Self-assessment documentation must remain current and internally consistent.

    Contractors should maintain a controlled record of:

    • The assessment methodology.
    • The score assigned to each applicable requirement.
    • The evidence supporting each score.
    • Known gaps and associated risk.
    • Plans of Action and Milestones (POA&Ms), where permitted.
    • Responsible personnel and target completion dates.
    • The current Supplier Performance Risk System (SPRS) score.
    • Annual affirmations and the basis for those affirmations.

    Compliance analyst reviewing a printed risk register beside dual monitors displaying a controls matrix

    A POA&M does not automatically cure a missing control or authorize a contractor to represent full implementation. Its use, acceptance, and effect depend on applicable requirements and contract terms.

    Management should also establish change control. A new application, cloud service, remote-access method, subcontractor, or network connection may change the system boundary and invalidate an older assessment.

    The assessment record should be understandable to an independent reviewer who did not prepare it. That standard helps reduce ambiguity during a prime contractor review, government inquiry, or government-led assessment.

    5. Preserve operational compliance, including incident reporting

    DFARS 252.204-7012 continues to establish important operational duties for covered contractors.

    Where the clause applies, contractors must implement the required security protections for covered contractor information systems and maintain procedures for cyber incident response. The clause also requires rapid reporting of qualifying cyber incidents. “Rapidly report” generally means reporting within 72 hours of discovery, subject to the specific clause and applicable reporting process.

    The organization should maintain:

    • A documented incident response plan.
    • Defined escalation responsibilities.
    • A method for determining whether CUI or a covered system was affected.
    • A clock for tracking the 72-hour reporting period.
    • Procedures for preserving relevant forensic information.
    • Contact and coordination procedures for the prime contractor and government.
    • Periodic exercises that test decision-making and reporting readiness.

    Technical controls and reporting procedures should be tested together. A contractor may have a written plan but still be unable to identify who must act, what information must be preserved, or how a report is initiated.

    The current DFARS clause text is available through Acquisition.gov. Contractors should review the version incorporated into the applicable contract.

    6. Align every representation with the implemented environment

    Cybersecurity representations must be consistent across proposals, contract certifications, SPRS submissions, annual affirmations, subcontractor questionnaires, and internal management reports.

    A contractor should establish a review process before submitting any statement that:

    • Claims compliance with DFARS 252.204-7012.
    • Describes a CMMC level or self-assessment status.
    • Identifies a specific SPRS score.
    • States that all required controls are implemented.
    • Describes a system as capable of handling CUI.
    • Confirms compliance on behalf of a subcontractor or service provider.

    Legal, contracts, information security, and program personnel should use the same source documentation. Differences between a proposal statement and the current assessment record should be investigated before submission.

    The False Claims Act creates potential exposure where a contractor knowingly or recklessly submits materially inaccurate information or conceals noncompliance. The risk does not require a third-party CMMC assessment to exist. Self-assessments and affirmations may still be relevant to responsibility, award, payment, and contract performance.

    A prudent contractor should not make a broader claim than the evidence supports.

    7. Prepare for review by the government, the prime, or an independent assessor

    The government retains authority to conduct its own assessment. A government assessment may take precedence over a contractor-provided self-assessment score.

    Contractors should therefore maintain assessment readiness even while third-party Phase 2 requirements are paused.

    Preparation should include:

    • A current system boundary diagram.
    • A complete and indexed evidence repository.
    • A responsible owner for each control area.
    • A record of open findings and remediation status.
    • A process for responding to information requests.
    • Controlled access to sensitive assessment materials.
    • Coordination procedures with prime contractors.
    • A method for documenting corrective actions.

    Clean fact graphic showing what the CMMC Phase 2 pause changes and what continues

    The pause may reduce a near-term third-party assessment requirement. It does not remove the need for disciplined cybersecurity governance. Contractors that maintain accurate records and operational controls will be better positioned for contract modifications, future rule changes, government review, and prime contractor oversight.

    What does the CMMC Phase 2 pause change?

    The September 3, 2026 revision changes the immediate treatment of certain third-party CMMC assessment requirements. Contracting officers are directed to remove or revise those requirements in applicable solicitations and contracts, subject to the stated modification process.

    It may permit Level 1 Self or Level 2 Self assessment approaches where the revised procurement documents allow them.

    What does the pause not change?

    The pause does not, by itself, remove:

    • Applicable DFARS 252.204-7012 obligations.
    • The NIST SP 800-171 Revision 2 baseline where required.
    • Self-assessment and SPRS reporting obligations.
    • Annual affirmation requirements.
    • Cyber incident reporting responsibilities.
    • Prime contractor flow-down requirements.
    • Government assessment authority.
    • Potential False Claims Act consequences for inaccurate representations.

    For additional background, contractors may review the DoD CIO CMMC resources and the NIST SP 800-171 Revision 2 publication.

    How JPI Worldwide can reduce compliance friction

    JPI Worldwide supports government agencies, prime contractors, and subcontractors with cybersecurity services, network infrastructure, technology integration, and operational support.

    As a subcontractor and technology infrastructure partner, JPI can help organizations:

    • Review technology environments that support contract performance.
    • Document system boundaries and infrastructure dependencies.
    • Organize assessment evidence and remediation priorities.
    • Support secure network configuration and monitoring.
    • Coordinate technical requirements across prime and subcontractor teams.
    • Improve operational readiness for remote, CONUS, and OCONUS environments.
    • Reduce avoidable friction between contracts, security, and technical personnel.

    JPI Worldwide does not provide a legal determination of compliance. Contract-specific obligations should be reviewed with qualified contracts and legal professionals.

    Government contractors, primes, and subcontractors may contact JPI Worldwide to discuss how cybersecurity services and infrastructure support may help address current assessment, documentation, and operational requirements.

    Sources

  • AI at the Tactical Edge: Practical Integration in Degraded Environments

    AI at the Tactical Edge: Practical Integration in Degraded Environments

    Page: JPI Worldwide Insights
    Revision date: August 31, 2026
    Author: Penny Marbel (JPI Worldwide)

    1. What does AI at the tactical edge mean?

    AI at the tactical edge means processing data and delivering AI-enabled support close to the point of use rather than depending entirely on a distant data center or continuously available cloud connection.

    AI at the tactical edge is the use of AI-enabled software, data, and computing resources near operational users and systems, with sufficient local capability to continue defined functions when communications are intermittent, limited, or unavailable.

    This model is relevant to government agencies, prime contractors, and subcontractors operating in remote, austere, or operationally sensitive environments. It may support activities such as:

    • Network and infrastructure monitoring.
    • Cybersecurity event triage.
    • Equipment maintenance and diagnostics.
    • Logistics and inventory analysis.
    • Document classification and knowledge retrieval.
    • Sensor and communications data aggregation.
    • Workflow automation and decision support.

    The tactical edge does not eliminate the need for enterprise systems. It changes where selected workloads are processed and how systems behave when connectivity cannot be assumed.

    The U.S. Department of Defense describes denied, degraded, intermittent, and limited connectivity as a condition that must be addressed in the design of modern operational systems. The Department of Defense Responsible Artificial Intelligence Strategy and Implementation Pathway also establishes that responsible AI requirements apply across the AI product lifecycle, including design, development, acquisition, deployment, and use.

    AI-enabled support process showing data ingestion, analysis, human review, orchestration, and outputs

    2. Why is cloud-only AI insufficient in degraded environments?

    Cloud services remain important for enterprise-scale storage, model development, centralized monitoring, and collaboration. However, a cloud-only architecture may create an operational dependency on bandwidth, latency, routing, power, and reach-back infrastructure.

    In degraded environments, those dependencies may affect system performance. A link may be unavailable for a defined period. Bandwidth may be insufficient for large data transfers. Latency may make a time-sensitive workflow impractical. A remote service may also be inaccessible because of maintenance, configuration, or security controls.

    A resilient architecture should therefore identify which functions must remain available locally.

    The objective is not to reproduce the entire enterprise environment at every edge location. The objective is to preserve essential functions through a controlled and documented local capability.

    A disconnected-first design may include:

    • Local data stores and approved knowledge resources.
    • Compressed or optimized models suitable for available compute.
    • Local identity and access controls.
    • Store-and-forward synchronization.
    • Health monitoring and local audit logs.
    • Clear rules for degraded operation.
    • Controlled synchronization when connectivity returns.

    When a link is restored, systems should synchronize selectively according to policy. They should not automatically transmit all available data without regard to classification, sensitivity, bandwidth, or mission need.

    3. What should a tactical edge AI architecture include?

    A practical architecture generally consists of five integrated layers.

    3.1 Data and communications inputs

    The system should identify the sources it is authorized to use. Sources may include network logs, sensor feeds, equipment status, ticketing systems, technical documentation, and operator inputs.

    Data should be normalized before it is used by an AI model. Poorly structured, incomplete, duplicated, or stale data can reduce the usefulness of an otherwise capable model.

    3.2 Local compute and storage

    Edge compute should be selected according to the use case, environmental conditions, available power, storage requirements, and sustainment plan. The system may use ruggedized hardware, compact servers, workstations, or other platforms appropriate to the operating environment.

    Hardware selection should not occur separately from application design. A model that performs well in an enterprise environment may require modification, compression, or a different inference strategy at the edge.

    3.3 AI and automation services

    AI services should have explicit purposes. Examples include anomaly classification, technical-document retrieval, event prioritization, maintenance recommendations, or workflow routing.

    The system should define what the AI may do, what it may recommend, and what it may not decide. This distinction is important for safety, accountability, and acquisition clarity.

    3.4 Human review and authorization

    Human review should remain part of the design for consequential workflows. AI output should be treated as decision support unless the applicable program documentation and governance process authorize a different level of automation.

    Operators should be able to understand the system’s status, limitations, confidence indicators, and available override or disengagement procedures. The DoD’s responsible AI principles identify reliability, traceability, and governability as essential characteristics of AI capabilities.

    3.5 Synchronization and enterprise integration

    The edge system should connect to enterprise services when permitted and technically feasible. Synchronization may include selected logs, model updates, configuration changes, approved data, and system-health information.

    Open interfaces and documented APIs can reduce integration friction for primes. They also support future technology changes without requiring unnecessary replacement of existing infrastructure.

    Disconnected-first edge AI architecture showing local processing, human review, logging, and selective synchronization

    4. How should cybersecurity be built into edge AI?

    Cybersecurity should be integrated before deployment. It should not be treated as a post-installation review.

    The NIST Special Publication 800-207, Zero Trust Architecture, defines zero trust as an approach that does not grant implicit trust based solely on network location or asset ownership. Authentication and authorization are performed before access to a resource is established.

    For tactical edge AI, this principle has practical implications:

    • Verify users and devices. Human and machine identities should be authenticated through approved controls.
    • Limit privileges. AI services, operators, administrators, and synchronization processes should receive only the access required for assigned functions.
    • Segment systems. Data, management, operational technology, and user services should be separated according to risk and mission requirements.
    • Protect data. Data should be encrypted in transit and at rest where applicable.
    • Record activity. Local logging should continue during connectivity outages and synchronize when authorized.
    • Control updates. Software, models, configurations, and policies should be signed, verified, and capable of rollback.
    • Plan for compromise. The design should include containment, recovery, and reconstitution procedures.

    Cybersecurity services for edge AI should address both the infrastructure and the model lifecycle. A secure network does not by itself ensure that training data, model updates, prompts, integrations, or AI outputs are trustworthy.

    5. What should contracting officers and primes require?

    Requirements should be written in measurable and operationally relevant terms. General language such as “provide an AI solution” does not adequately define performance, limitations, integration responsibilities, or acceptance criteria.

    A solicitation, statement of work, or subcontract work package should address:

    1. Defined use cases. Identify the workflow, user population, data sources, operating conditions, and prohibited uses.
    2. Degraded-mode behavior. State which functions must continue during disconnected, bandwidth-limited, or partially failed conditions.
    3. Interface requirements. Require documented APIs, data formats, identity dependencies, and integration points.
    4. Security controls. Identify access control, logging, encryption, segmentation, update, and incident-response requirements.
    5. Test and evaluation. Require testing under representative latency, bandwidth, power, environmental, and cybersecurity conditions.
    6. Human oversight. Define approval, escalation, override, disengagement, and reporting procedures.
    7. Data and model documentation. Require appropriate descriptions of data provenance, model limitations, versioning, performance boundaries, and update history.
    8. Sustainment. Define training, field support, spare equipment, patching, monitoring, configuration management, and technical documentation.
    9. Acceptance evidence. Specify what test results, logs, demonstrations, and deliverables establish compliance.

    The DoD Responsible AI Strategy and Implementation Pathway identifies acquisition lifecycle management, requirements validation, test and evaluation, workforce preparation, and continuous oversight as connected responsibilities. Primes should therefore evaluate an AI subcontractor on more than a demonstration. Integration discipline, documentation, field support, cybersecurity coordination, and sustainment capacity may determine whether the capability reduces or increases program friction.

    Tactical edge AI integration controls covering definition, protection, validation, and sustainment

    6. What is a practical integration process?

    A controlled implementation may follow this sequence:

    • Define the mission requirement. Establish the operational problem before selecting a model or vendor.
    • Map the system boundary. Identify users, devices, networks, data sources, external services, and authorization points.
    • Select the edge workload. Keep only the data and functions that must operate locally.
    • Prepare the data. Normalize, label, filter, and govern data before model deployment.
    • Integrate cybersecurity controls. Apply identity, access, segmentation, encryption, logging, and update controls.
    • Test under stress. Evaluate behavior during link loss, reduced bandwidth, equipment failure, malicious input, and data degradation.
    • Train users and maintainers. Explain intended use, limitations, escalation procedures, and failure modes.
    • Monitor and improve. Review performance, operator feedback, security events, and model changes throughout the lifecycle.

    The process should produce a documented baseline. That baseline may include architecture diagrams, interface definitions, operating procedures, test results, model or data cards, configuration records, and sustainment responsibilities.

    7. How can JPI Worldwide support a prime or government program?

    JPI Worldwide provides AI and systems integration, network engineering, cybersecurity, communications, technical staffing, logistics, and field deployment support. These capabilities can be combined to address the practical dependencies that affect edge AI implementation.

    For primes and contracting officers, JPI may support:

    • AI-enabled workflow and process automation.
    • Agent and systems integration.
    • Data aggregation and operational visibility.
    • Network and communications integration.
    • Secure remote-access and infrastructure implementation.
    • Field installation, commissioning, troubleshooting, and training.
    • Technical personnel for CONUS and OCONUS requirements.
    • Deployment coordination and sustainment support.

    JPI’s experience across government, commercial, humanitarian, and international operating environments informs an approach based on the full operating requirement, including infrastructure, personnel, logistics, cybersecurity, and post-deployment support.

    Contact JPI Worldwide

    Organizations evaluating AI at the tactical edge, defense IT solutions, or cybersecurity services may contact JPI Worldwide to discuss a business, agency, or department requirement.

    Do not submit classified information, Controlled Unclassified Information, export-controlled technical data, passwords, credentials, or other sensitive material through the public contact form. A secure communications method should be requested when the requirement requires one.

    Sources and further reading

  • Staffing the Mission: Sourcing Technical Personnel for CONUS and OCONUS Deployments

    Staffing the Mission: Sourcing Technical Personnel for CONUS and OCONUS Deployments

    Page: JPI Worldwide Insights
    Revision date: August 31, 2026
    Author: Penny Marbel (JPI Worldwide)

    1. The staffing requirement is part of the technical solution

    Technical infrastructure does not operate independently of the people assigned to deploy, integrate, maintain, and support it. A network may be properly designed, but performance can still be affected by staffing gaps, incomplete mobilization, unclear responsibilities, or insufficient field experience.

    For government agencies, prime contractors, and nonprofit organizations, technical staffing may determine whether a project transitions from procurement to operational capability without avoidable delays.

    Key definition: Technical staffing for CONUS and OCONUS deployments is the structured sourcing, qualification, mobilization, and sustainment of personnel needed to install, operate, protect, troubleshoot, and hand off technology in domestic or overseas environments.

    The staffing model may include:

    • Network and systems technicians
    • Communications and infrastructure specialists
    • Cybersecurity personnel
    • Field service engineers
    • Installation and commissioning teams
    • Technical project managers
    • Trainers and end-user support personnel
    • Vendor-certified or platform-specific specialists
    • Personnel with applicable safety, medical, aviation, logistics, or other field qualifications

    JPI Worldwide provides technical staffing and field services for short-duration deployments, project-based requirements, and sustained operations in CONUS and OCONUS environments.

    2. What makes CONUS and OCONUS staffing different?

    CONUS work may still involve complex travel, distributed sites, regulated facilities, and difficult labor-market conditions. OCONUS work adds additional considerations. These may include transportation, customs, local infrastructure, personnel documentation, security requirements, medical readiness, communications limitations, and support in areas where replacement personnel are not readily available.

    A staffing plan should therefore address more than the technical labor category. It should account for the conditions under which personnel will perform.

    A practical deployment staffing component

    A useful staffing component should evaluate each position against five requirements:

    1. Technical scope
      Identify the systems, networks, communications equipment, software, facilities, and interfaces the personnel will support.

    2. Field conditions
      Define whether the work involves a conventional office, industrial site, temporary facility, remote location, or austere operating environment.

    3. Readiness requirements
      Identify required training, screening, certifications, clearances, travel documents, medical requirements, and customer-specific approvals.

    4. Coverage model
      Establish whether support will be remote, on-site, shift-based, on-call, rotational, surge, or a combination of these models.

    5. Sustainment and handoff
      Define maintenance, troubleshooting, documentation, training, replacement coverage, and transition responsibilities after installation.

    Deployment staffing planning table with generic coverage, skills, readiness, and sustainment categories in a field operations office

    This component helps primes and mission partners compare candidates against the actual operating requirement rather than relying solely on resumes or job titles.

    3. How should primes source technical personnel?

    Primes should source personnel against the performance requirement, not only against an isolated labor category. The relevant question is not simply whether a candidate has experience with a technology. The question is whether that person can apply the experience within the schedule, location, security framework, reporting structure, and operational conditions of the contract.

    A prime contractor’s staffing review should consider:

    • Experience with the required technical environment
    • Ability to work within a larger integrated team
    • Documented field installation or troubleshooting experience
    • Familiarity with configuration control and technical documentation
    • Ability to work with government, commercial, local, and subcontractor personnel
    • Readiness for travel and overseas deployment, where applicable
    • Availability for rotations, surge support, or sustained operations
    • Understanding of customer reporting and quality requirements
    • Ability to perform a disciplined handoff to local or follow-on personnel

    This approach reduces operational friction for the prime. It also creates clearer accountability between the prime, subcontractor, government customer, and technical workforce.

    Federal service requirements are commonly written around measurable outcomes. FAR 37.602 provides that a performance work statement should describe required results and establish standards that permit performance assessment. Staffing decisions should support those standards.

    For example, a requirement may measure:

    • Network availability
    • Ticket response and resolution
    • Installation completion
    • Configuration accuracy
    • Patch or maintenance timelines
    • Documentation quality
    • Training completion
    • Service continuity during personnel transitions

    The specific measures must come from the applicable contract, statement of work, or performance work statement. A staffing provider should not assume that a general technician profile satisfies every program requirement.

    4. How does the model apply to NGOs and development organizations?

    NGOs and international development organizations may require many of the same technical functions as government and defense programs, but the operating objectives may differ.

    A development or humanitarian program may require:

    • Connectivity for a field office or medical facility
    • Network installation for an education or governance program
    • Communications support for mobile teams
    • Technical training for local personnel
    • Internet or broadband service in an infrastructure-limited area
    • Equipment staging and movement
    • Field troubleshooting and maintenance
    • Technology support during program expansion or emergency response

    The operating environment may be remote without being military. Staffing may involve international personnel, locally engaged staff, third-country personnel, commercial technicians, or a blended team. The appropriate model depends on the scope of work, local law, security conditions, funding requirements, and the organization’s duty-of-care procedures.

    JPI Worldwide describes its humanitarian and international-development support as including communications, infrastructure, technical staffing, logistics, and operational support for organizations working in complex environments.

    The same core principle applies across both tracks:

    Personnel should be selected for the environment in which the work must be performed, not only for the technology being installed.

    Technical personnel working with communications and office equipment in a real-world field support setting

    5. What compliance and deployment issues should be reviewed?

    Overseas technical staffing requires contract-specific review. No single rule determines every requirement. The applicable contract clauses, place of performance, customer, personnel status, and mission conditions must be evaluated together.

    Overseas workers’ compensation

    The U.S. Department of Labor’s Defense Base Act guidance explains when workers’ compensation coverage may apply to employees working overseas on covered government contracts and related work.

    A contractor or subcontractor should determine, before deployment:

    • Whether the contract is covered by the Defense Base Act
    • Which personnel are covered
    • Whether any waiver or local-law treatment applies
    • Whether insurance is active before covered work begins
    • Whether required notices and records are maintained

    The DBA is not a staffing-level rule. It is an employee-protection and insurance requirement that may affect the cost, timing, and administration of an overseas deployment.

    Government and customer deployment requirements

    Where personnel support U.S. Armed Forces outside the United States, DFARS 252.225-7040 may establish additional requirements concerning contractor personnel, authorization, tracking, training, and deployment readiness.

    Where applicable, the contractor should also review:

    • Letter of authorization requirements
    • Security and background screening
    • Medical screening and immunizations
    • Personal security and law-of-war training
    • Country or theater clearances
    • Travel and movement procedures
    • Government-furnished housing, transportation, or security
    • Reporting requirements for deployed personnel

    FAR 52.225-19 addresses contractor personnel performing in a designated operational area or supporting a diplomatic or consular mission outside the United States. The clause may assign logistical and security responsibilities to the contractor unless the contract provides otherwise.

    These provisions should be reviewed by the responsible contracts, legal, human resources, insurance, and program-management personnel. General guidance does not replace contract-specific advice.

    Rugged field facility and communications equipment supporting technical deployment logistics

    6. How can staffing reduce operational friction for a prime?

    A subcontractor reduces friction when it provides more than a resume. The subcontractor should provide a usable staffing package that allows the prime to make timely decisions and integrate the personnel into the program.

    That package may include:

    • Candidate qualifications mapped to the statement of work
    • Availability and proposed mobilization timeline
    • Deployment-readiness status
    • Required certifications and training
    • Travel and rotation assumptions
    • Labor category and rate information
    • Replacement or backfill procedures
    • Technical reporting responsibilities
    • Equipment and tool requirements
    • Handoff and continuity procedures

    The prime should also confirm how staffing changes will be controlled. A technically qualified replacement may still require customer approval, new travel arrangements, additional training, or an updated authorization.

    JPI Worldwide’s government support capabilities include technical personnel, field installation, systems integration, troubleshooting, training, maintenance, logistics, and deployment support. This allows staffing to be considered alongside the network deployment services and infrastructure requirements that the personnel will support.

    7. What should a deployment staffing plan contain?

    A deployment staffing plan should be concise, specific, and traceable to the contract requirement. At a minimum, it should identify:

    • Mission objective
    • Place and period of performance
    • Required technical functions
    • Personnel qualifications
    • Coverage and shift assumptions
    • Mobilization sequence
    • Equipment and tool requirements
    • Training and readiness obligations
    • Security and access dependencies
    • Travel and logistics responsibilities
    • Escalation procedures
    • Documentation and handoff requirements
    • Sustainment and replacement coverage

    The plan should distinguish between confirmed facts, customer-provided assumptions, and items requiring approval. This distinction is particularly important when the work involves overseas travel, controlled facilities, sensitive systems, or changing field conditions.

    8. How does JPI Worldwide support technical staffing?

    JPI Worldwide can support primes, government customers, NGOs, development organizations, and commercial partners with technical personnel for:

    • Network deployment services
    • Communications and infrastructure installation
    • Systems integration
    • Cybersecurity implementation and support
    • Field troubleshooting
    • Technical training
    • Preventive and corrective maintenance
    • Commissioning and operational testing
    • Sustained technical operations
    • Logistics and deployment coordination

    JPI’s published experience includes government, commercial, humanitarian, development, and international operating environments. The company’s role may be structured as a focused technical assignment, an integrated subcontract function, or a broader field-support requirement.

    Staffing remains subject to the applicable statement of work, contract terms, customer approvals, personnel availability, legal requirements, and conditions at the place of performance. No staffing model should be treated as universal.

    JPI Worldwide technical team supporting a field deployment in a real operational setting

    Frequently asked questions

    What is the difference between CONUS and OCONUS technical staffing?

    CONUS staffing supports work within the contiguous United States. OCONUS staffing supports work outside the contiguous United States. OCONUS assignments may involve additional travel, logistics, insurance, security, training, documentation, and local operating requirements.

    What technical personnel may be required for an overseas deployment?

    The requirement may include network technicians, systems administrators, communications specialists, cybersecurity personnel, field service engineers, project managers, trainers, or vendor-certified specialists. The appropriate labor mix depends on the contract and technical scope.

    Does the Defense Base Act determine how many IT personnel must be deployed?

    No. The Defense Base Act concerns workers’ compensation coverage for certain overseas work. Staffing levels and technical qualifications are generally defined by the applicable contract, statement of work, performance work statement, or customer requirement.

    How can a prime contractor use a staffing subcontractor?

    A prime may use a staffing subcontractor to provide qualified personnel, surge support, field installation, technical integration, sustainment, or specialized expertise. The subcontract should define scope, deliverables, reporting, responsibility for deployment costs, and replacement procedures.

    What should an NGO assess before sending technical personnel overseas?

    An NGO should assess the technical requirement, local operating conditions, personnel safety, travel and insurance obligations, communications dependencies, equipment movement, local support, training, and sustainment. The organization should also confirm that the staffing plan is consistent with its program obligations and applicable law.

    Discuss the requirement with JPI Worldwide

    JPI Worldwide supports organizations that require technical personnel able to deploy, integrate, troubleshoot, and sustain systems in CONUS and OCONUS environments.

    To discuss a staffing, network deployment, field support, or technical integration requirement, use the JPI Worldwide contact page, email connect@jpiworldwide.com, or call +1-509-210-3023.

    Do not submit classified information, Controlled Unclassified Information, export-controlled technical data, passwords, credentials, or other sensitive material through a public contact form.

  • How to Build a DCAA-Compliant Accounting System: A Field Guide for Subs

    How to Build a DCAA-Compliant Accounting System: A Field Guide for Subs

    Page label: Government Contractors
    Revision date: August 31, 2026
    Author: Penny Marbel (JPI Worldwide)

    A subcontractor supporting federal work must be able to show where costs came from, which contract received the charge, how indirect costs were allocated, and whether claimed costs are allowable under the contract.

    This requirement applies even when accounting is managed by a small team. A basic commercial accounting platform may be useful, but software alone does not establish an adequate government-contracting accounting system.

    1. What Does “DCAA-Compliant” Mean?

    “DCAA-compliant” is an informal term. The Defense Contract Audit Agency does not approve or certify accounting software.

    A more precise definition is:

    A DCAA-compliant accounting system is a system of policies, procedures, controls, records, and software that provides reasonable assurance that costs are recorded accurately, allocated consistently, supported by documentation, and charged in accordance with applicable laws, regulations, and contract terms.

    For covered Department of Defense contracts, DFARS 252.242-7006 describes an acceptable accounting system as one that provides reasonable assurance that:

    • Applicable laws and regulations are followed.
    • Accounting records and cost data are reliable.
    • The risk of misallocation and mischarging is minimized.
    • Contract charges are consistent with billing procedures.

    The system may include multiple connected components, including the general ledger, job-cost ledger, labor distribution system, timekeeping platform, billing process, purchasing records, and document-retention controls.

    The applicable requirements depend on the contract type, agency, clauses included in the prime contract and subcontract, and whether Cost Accounting Standards apply.

    2. Which Rules Should a Subcontractor Review?

    A subcontractor should begin with the actual subcontract and the clauses incorporated into it. The system should then be mapped against the applicable regulatory requirements.

    The principal sources generally include:

    A subcontractor should not assume that a commercial firm-fixed-price subcontract has the same accounting requirements as a cost-reimbursement subcontract. At the same time, a firm-fixed-price arrangement may still require cost information for pricing, change proposals, audits, or prime-contractor oversight.

    3. How Should the Accounting System Be Designed?

    The accounting system should be designed around final cost objectives. In most government contracts, the final cost objective is the contract, task order, delivery order, or another identifier required by the contract.

    A practical design process includes the following steps.

    Step 1: Create a contract and clause map

    For each subcontract, record:

    • Contract and task-order identifiers.
    • Period of performance.
    • Contract type.
    • Funding or ceiling limitations.
    • Billing frequency and format.
    • Labor categories and approved rates.
    • Required contract line-item detail.
    • Advance-approval requirements.
    • Audit, records-access, and flowdown provisions.
    • Applicable indirect-rate requirements.

    This contract brief should be available to accounting, contracts, program management, and employees who record time or expenses.

    Step 2: Build a controlled chart of accounts

    The chart of accounts should distinguish among:

    • Direct labor.
    • Direct materials.
    • Direct travel.
    • Other direct costs.
    • Subcontract and vendor costs.
    • Overhead pools.
    • General and administrative expenses.
    • Unallowable costs.
    • Credits, rebates, and refunds.

    The general ledger should control the job-cost ledger. Costs recorded in subsidiary systems should reconcile to the general ledger at defined intervals, normally at least monthly where applicable.
    Step 3: Establish written cost classifications

    A written policy should explain when a cost is direct and when it is indirect.

    Under FAR 31.202, a cost identified specifically with a contract should generally be charged directly to that contract. Under FAR 31.203, indirect costs are allocated to intermediate or final cost objectives based on a logical relationship and the benefits received.

    The same type of cost should not be treated as direct for one contract and indirect for another under similar circumstances. Limited exceptions may exist for minor costs when the treatment is consistently applied and produces substantially the same result.

    4. What Timekeeping Controls Are Required?

    Timekeeping is one of the most important controls for government contractors because labor charges may represent a significant portion of total contract cost.

    Employees should record all hours worked daily, including time spent on:

    • Each assigned contract or task order.
    • Internal or indirect activities.
    • Training.
    • Leave and other compensated absences.
    • Uncompensated overtime, where applicable.
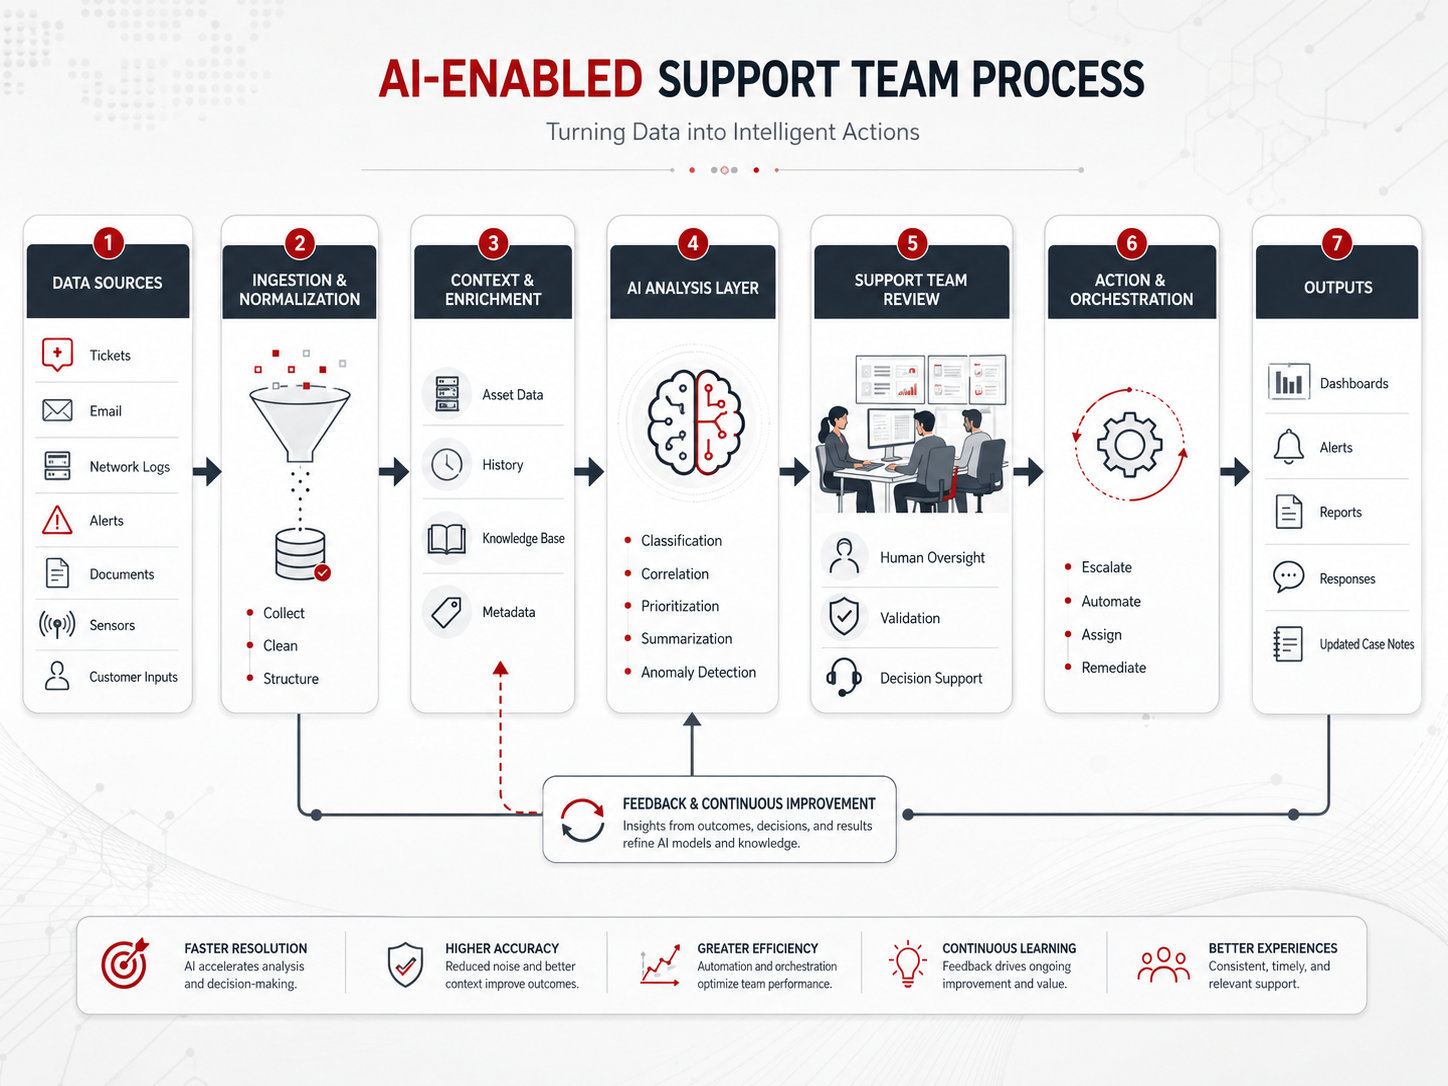
    Employees should certify their own time. Supervisors should review and approve timecards. A supervisor should not routinely complete an employee’s timecard.

    Corrections should preserve the original entry, identify the revised entry, state the reason for the correction, and document employee concurrence where required by company procedure.

    Subcontractor employee entering daily time on a laptop with project records and approval materials

    The labor distribution system should reconcile to payroll records and trace to the job-cost ledger and general ledger. The system should also support a floor check or employee interview by showing how recorded time corresponds to actual work activity.

    A field deployment may create access limitations. If personnel cannot access the normal electronic timekeeping system, the subcontractor should establish a documented alternate process. The alternate process should preserve daily accuracy, employee certification, supervisory review, and later entry into the controlled system.

    5. How Should Indirect Costs Be Allocated?

    Indirect costs should be grouped into logical pools and allocated using an appropriate base.

    Common pools may include:

    • Fringe benefits.
    • Engineering overhead.
    • Site or project overhead.
    • Material handling.
    • General and administrative expenses.

    Examples of allocation bases include direct labor dollars, direct labor hours, direct material dollars, or total cost input. The selected base should have a reasonable relationship to the costs in the pool.

    For example, an engineering overhead pool may be allocated over engineering direct labor. A G&A pool may be allocated over an appropriate total-cost-input or value-added base, depending on the company’s operations and applicable requirements.

    The number of pools should reflect the business. A small subcontractor may require only one overhead pool and one G&A pool. A more complex organization may require several pools for distinct functions or operating locations.

    The method should be documented and applied consistently. A significant change in business volume, subcontracting, facilities, products, or operating structure may require the allocation methodology to be reassessed.

    6. How Are Unallowable Costs Controlled?

    A subcontractor must identify and exclude unallowable costs from applicable billings, claims, proposals, and indirect-rate calculations.

    FAR 31.201-6 requires expressly unallowable and mutually agreed-upon unallowable costs to be identified and excluded. Directly associated costs may also require exclusion.

    Examples of costs that may be unallowable under specific circumstances include:

    • Entertainment.
    • Certain advertising and promotional expenses.
    • Bad debts.
    • Interest and other financial costs.
    • Fines and penalties.
    • Contributions or donations.
    • Certain legal and proceeding-related costs.
    • Costs exceeding applicable contract or regulatory limitations.

    A policy should define review responsibility, account coding, approval requirements, and corrective action. Unallowable costs should be separately identified in the books or through another readily reconcilable method.

    Hands organizing invoices, receipts, and general ledger records in a controlled accounting workspace

    7. How Should Billing and Monthly Close Be Controlled?

    Billing should be based on recorded, allowable, allocable, and properly supported costs. The amount billed should not exceed contract ceilings, funding limitations, approved rates, or other contractual restrictions.

    A monthly close process should include:

    1. Posting payroll and labor distribution.
    2. Reconciling timekeeping to payroll.
    3. Reconciling job costs to the general ledger.
    4. Reviewing direct and indirect classifications.
    5. Screening for unallowable costs.
    6. Calculating or updating indirect rates.
    7. Comparing cumulative costs with contract limitations.
    8. Reconciling booked costs to billed costs.
    9. Documenting adjusting entries.
    10. Retaining supporting records.

    Where FAR 52.216-7 applies, final indirect cost rate proposals generally must be submitted within six months after the end of the contractor’s fiscal year unless an extension is granted in writing.

    The clause also addresses completion vouchers and updates to billings after final rates are settled. A subcontractor should maintain records that allow the prime contractor to obtain accurate subcontract cost information and complete its own reporting obligations.

    8. What Should a First-Time Subcontractor Test Before Award?

    A first-time subcontractor should conduct a documented self-assessment before incurring significant contract costs.

    The assessment should answer these questions:

    • Can the system accumulate costs by contract, task order, and required line item?
    • Can direct and indirect costs be separated?
    • Are indirect pools and allocation bases documented?
    • Are unallowable costs identified and excluded?
    • Do employees complete and certify time daily?
    • Do supervisors approve timecards?
    • Can labor distribution reconcile to payroll and the general ledger?
    • Are adjusting entries approved and supported?
    • Can invoices be reconciled to current and cumulative cost records?
    • Are records retained and retrievable?
    • Can the company explain its system to a prime contractor, contracting officer, or auditor?

    Finance and program-management professionals conducting an internal accounting system review in a conference room

    The objective is not to purchase a product labeled “DCAA-compliant.” The objective is to implement a controlled process that can be explained, operated, tested, and supported with records.

    9. How JPI Worldwide Can Support Subcontractor Operations

    A subcontractor’s accounting controls are part of broader operational readiness. Personnel, technology, logistics, field deployment, procurement, and contract administration must remain coordinated.

    JPI Worldwide supports government agencies, prime contractors, and subcontractors with technical infrastructure and integrated capabilities, including communications, networking, cybersecurity, AI and systems integration, technical staffing, logistics, and field services. JPI also supports government and contractor teams in CONUS and OCONUS environments.

    JPI’s role may include technical deployment, field support, systems integration, logistics coordination, or other defined subcontract requirements. These services can help reduce operational friction for primes that require a reliable partner able to support work from planning through deployment and sustainment.

    To discuss how JPI Worldwide may help support your business, agency, or department, use the JPI contact page or email connect@jpiworldwide.com. Do not submit classified information, Controlled Unclassified Information, export-controlled technical data, passwords, credentials, or other sensitive material through the public contact form.

    Sources and Administrative Notice

    This article is provided for informational purposes. It is not legal, accounting, audit, or contract-specific advice. Requirements may vary by agency, contract type, subcontract terms, applicable clauses, and current regulatory guidance. Contractors should review the governing contract and obtain qualified professional advice where appropriate.

  • Satellite Communications for Modern Missions: Starlink, Ku-Band, and Custom Rigs

    Satellite Communications for Modern Missions: Starlink, Ku-Band, and Custom Rigs

    Page: Technology Infrastructure and Mission Support
    Revision date: August 31, 2026
    Author: Penny Marbel (JPI Worldwide)

    Satellite communications are one component of a broader telecom infrastructure requirement. A terminal, antenna, or modem does not provide a complete operational capability by itself. The system must also connect to local networks, support cybersecurity controls, operate within available power, and remain maintainable after deployment.

    Starlink, managed Ku-band services, and custom communications rigs may each have a legitimate role. The appropriate selection depends on coverage, mission traffic, regulatory conditions, physical environment, security requirements, logistics, and the level of operational control required.

    Satellite communications are the use of space-based communications systems to exchange voice, data, video, or network traffic between geographically separated users and network points.

    For primes and mission partners, the principal issue is often not the satellite service alone. It is whether the subcontractor can integrate that service into a dependable, documented, and supportable technology package.

    1. What Role Does Satellite Communications Play in Telecom Infrastructure?

    Satellite communications may extend or supplement terrestrial networks where fiber, cellular service, microwave links, or fixed broadband are unavailable, limited, or unsuitable.

    A complete remote connectivity solution may include:

    • Satellite terminals and antennas
    • Modems, routers, and firewalls
    • Local-area and wide-area networking
    • Power conditioning, backup power, and grounding
    • Network segmentation and secure remote access
    • Monitoring and troubleshooting tools
    • Equipment staging, transportation, and installation
    • User training, documentation, and sustainment

    The satellite link is therefore best treated as a transport layer within a larger architecture. It may serve as a primary connection, a backup path, or one element of a multi-path design.

    JPI Worldwide provides network engineering and infrastructure support across wired, wireless, radio, broadband, and satellite-connected environments. This broader approach is relevant when a prime contractor needs a technical partner that can execute more than terminal installation.

    Technicians integrating communications equipment in a temporary operations room

    2. How Does Starlink Fit Into a Modern Communications Architecture?

    Starlink is a low Earth orbit, or LEO, satellite network. According to Starlink’s technical information, its satellites operate at approximately 550 kilometers above Earth and are designed to provide lower latency than traditional geostationary systems.[1]

    A LEO architecture can support interactive applications such as voice, video conferencing, cloud access, and enterprise network traffic where service is available and the terminal has a suitable view of the sky. Starlink also identifies Ku-band phased-array antennas as part of its satellite design.[1]

    For a prime or agency evaluating Starlink, the relevant question is not whether the service is technically capable. The question is how the service will be used within the approved network design.
    Potential applications may include:

    • Primary broadband at a temporary or remote facility
    • Backup connectivity for a terrestrial network
    • Rapidly deployable internet access
    • Temporary augmentation during infrastructure disruption
    • A transport path for SD-WAN or policy-based routing
    • Connectivity for field offices, project teams, or support locations

    Starlink should not be treated as an unconditional substitute for all other communications methods. Availability, service-plan terms, regulatory permissions, geographic coverage, obstructions, weather, power, network policy, and physical protection may affect performance.

    The Federal Communications Commission maintains the regulatory record for Starlink operations in the United States. FCC authorizations address spectrum use, orbital parameters, interference protection, and other operating conditions.[2]

    Accordingly, project teams should document:

    • The intended service area and applicable authorization requirements
    • The expected user population and traffic profile
    • Power and environmental conditions
    • Mounting, cable-routing, and physical-protection requirements
    • Network-security boundaries
    • Failover procedures if the service becomes unavailable

    3. What Is Ku-Band, and When Is It Appropriate?

    Ku-band is a portion of the radio-frequency spectrum commonly used for satellite communications. The International Telecommunication Union identifies satellite allocations and coordination requirements through the Radio Regulations, including provisions affecting fixed-satellite service, geostationary systems, and non-geostationary systems.[3]

    Ku-band does not describe one specific product or orbit. A Ku-band system may use a geostationary satellite, a non-geostationary constellation, or a custom configuration designed around a particular operator and terminal.

    Geostationary Earth orbit, or GEO, is approximately 35,786 kilometers above the equator. GEO satellites appear relatively fixed from the ground, which can simplify antenna pointing and provide broad coverage. The greater distance, however, generally creates higher latency than LEO systems.

    Managed Ku-band services may remain appropriate where the requirement emphasizes:

    • Established satellite-operator relationships
    • Broad and predictable geographic coverage
    • Dedicated or managed bandwidth
    • Broadcast, trunking, or fixed backhaul
    • Compatibility with existing teleport or hub infrastructure
    • A service model with defined operational responsibilities

    Performance depends on the specific satellite, service plan, antenna, modem, link budget, weather conditions, network contention, and configuration. No single Ku-band label establishes a guaranteed result.

    Clean comparison graphic showing LEO, GEO, terrestrial, and multi-path connectivity layers

    4. What Is a Custom Satellite Communications Rig?

    A custom rig is an integrated communications package configured for a defined operating environment. It may use Ku-band, C-band, LEO, or more than one transport method. The defining feature is not the antenna. It is the integration of the complete system.

    A custom rig may include:

    • An antenna, terminal, or stabilized mounting system
    • Satellite modem and radio-frequency equipment
    • Ruggedized transport cases or equipment enclosures
    • Power distribution, conditioning, and backup power
    • Router, firewall, switches, and wireless access points
    • Network monitoring and out-of-band management
    • Environmental controls and cable protection
    • Spares, tools, and replacement components
    • Installation documentation and test procedures

    Custom designs may be necessary when the system must fit a constrained vehicle, temporary facility, remote office, industrial site, or mobile operating platform. They may also be appropriate where the customer requires multiple communications paths with controlled failover.

    A custom rig generally requires more engineering and preparation than a standard commercial terminal. The tradeoff may be greater control over equipment selection, network policy, redundancy, maintainability, and integration with existing telecom infrastructure.

    5. How Do Starlink, Ku-Band, and Custom Rigs Compare?

    Consideration Starlink or similar LEO service Managed GEO Ku-band Custom communications rig
    Primary strength Lower-latency broadband where available Broad coverage and managed backhaul Tailored integration and control
    Deployment profile Often suitable for rapid installation Requires planned service and antenna configuration Requires engineering, staging, and testing
    Network role Primary, backup, or augmentation Primary, backup, or fixed backhaul Multi-path or mission-specific architecture
    Key constraints Coverage, obstructions, power, policy, and service terms Latency, antenna pointing, link budget, and weather Cost, logistics, engineering, and sustainment
    Prime-contractor value Fast connectivity option Managed and established transport layer Integrated work package with defined interfaces

    The selection should be based on the mission requirement rather than the popularity of a particular platform. A hybrid architecture may use LEO for interactive traffic, GEO for additional coverage or backhaul, and terrestrial services where available.

    The architecture should also define how traffic moves when one path degrades. Failover is not established merely by installing two terminals. Routing policy, monitoring, authentication, power, physical cabling, and user procedures must support the intended continuity plan.

    6. Why Does Telecom Infrastructure Integration Matter?

    Remote communications projects frequently fail at the interfaces between disciplines. The satellite provider may be responsible for the service. A separate contractor may manage the facility. Another team may control cybersecurity, network access, power, logistics, or user support.
    Without clear responsibility, the prime may inherit unresolved questions involving:

    • Who owns the local network configuration
    • Who validates firewall and routing rules
    • Who provides power and grounding
    • Who performs acceptance testing
    • Who documents the final configuration
    • Who responds to service degradation
    • Who stages spares and replacement equipment
    • Who coordinates technical personnel and transportation

    JPI Worldwide can support primes and mission partners through communications and satellite integration, technical staffing, cybersecurity implementation, network engineering, logistics, and field deployment.

    This model may reduce operational friction by consolidating related technical activities under a defined subcontract scope. It may also help a prime coordinate engineering, field personnel, equipment movement, installation, troubleshooting, and sustainment without creating unnecessary handoffs.

    JPI’s experience includes support for government, commercial, humanitarian, and international programs in CONUS and OCONUS environments. Project-specific details remain subject to applicable authorization, disclosure, security, and contractual restrictions.

    Network operations personnel reviewing infrastructure status in a secure technical environment

    7. What Should a Prime Evaluate Before Selecting a Satcom Subcontractor?

    A prime should evaluate the subcontractor’s ability to manage the complete deployment lifecycle.

    The evaluation should address:

    1. Requirements definition. Can the subcontractor translate user, traffic, coverage, and availability requirements into an engineering plan?

    2. Network integration. Can the subcontractor connect the satellite service to the required LAN, WAN, firewall, wireless, and monitoring environments?

    3. Cybersecurity. Can the subcontractor apply segmentation, access control, secure remote access, hardening, and configuration documentation?

    4. Field execution. Can qualified personnel install, test, troubleshoot, train users, and support corrective maintenance?

    5. Logistics. Can the subcontractor coordinate equipment staging, movement, site access, replacement components, and personnel mobilization?

    6. Regulatory coordination. Can the project team identify applicable spectrum, customs, import, export, and host-country requirements before shipment or activation?

    7. Sustainment. Can the subcontractor provide a support model after installation, including escalation procedures, spares, monitoring, and configuration control?

    JPI Deployment Component

    JPI can serve as the technical integration component within a prime’s broader delivery model. The scope may include system design, equipment preparation, network integration, field installation, cybersecurity implementation, acceptance testing, technical staffing, logistics coordination, and operational support.

    The exact scope should be defined by the statement of work, security requirements, service location, customer architecture, and applicable law.

    8. Frequently Asked Questions

    Is Starlink a replacement for all other satellite communications?

    No. Starlink may be suitable for specific broadband and low-latency requirements. GEO Ku-band, terrestrial services, radio systems, and other transports may remain necessary for coverage, redundancy, specialized traffic, or continuity planning.

    Is Ku-band obsolete because LEO services are expanding?

    No. Ku-band remains a widely used satellite communications spectrum with established commercial and government applications. The relevant choice is the complete system architecture, not the band name alone.

    Does a second terminal automatically provide network redundancy?

    No. Redundancy requires independent paths, compatible power systems, routing and failover policies, monitoring, tested procedures, and personnel who understand the recovery process.

    What can JPI provide to a prime contractor?

    JPI may provide communications integration, network infrastructure, cybersecurity, technical personnel, logistics, deployment support, and sustained field services. Requirements should be reviewed before any commitment is made.

    9. Contact JPI Worldwide

    Primes, partners, government agencies, and departments evaluating satellite communications or broader telecom infrastructure may contact JPI Worldwide to discuss the technical and operational requirement.

    JPI can review:

    • Remote connectivity and network architecture
    • Starlink or managed satellite integration
    • Ku-band and custom communications rigs
    • Redundant and multi-path connectivity
    • Cybersecurity and secure network access
    • Field deployment and technical staffing
    • Equipment staging, logistics, and sustainment

    Use the JPI Worldwide contact page or email connect@jpiworldwide.com. Do not submit classified information, Controlled Unclassified Information, export-controlled technical data, passwords, credentials, or other sensitive material through the public contact form.

    Sources

    1. Starlink, Satellite Technology
    2. FCC, SpaceX Gen2 Starlink Authorization, FCC 22-91
    3. International Telecommunication Union, Radio Regulatory Framework for Space Services
    4. JPI Worldwide, Capabilities
    5. JPI Worldwide, Experience