Category: Civilian Contractors

  • OFAC, ITAR, and Customs: What It Takes to Move Technology Into an Austere Theater

    OFAC, ITAR, and Customs: What It Takes to Move Technology Into an Austere Theater

    Page: JPI Worldwide Insights
    Revision date: August 31, 2026
    Author: Penny Marbel (JPI Worldwide)

    Moving communications equipment, network infrastructure, cybersecurity tools, and other technology into an overseas or austere theater requires more than transportation planning.
    The movement may implicate sanctions controls, export-control authorization, customs requirements, carrier rules, host-nation procedures, and contract-specific obligations.

    For government buyers, prime contractors, and subcontractors, the central requirement is coordination. A shipment may be technically ready but unable to move because the consignee is not properly documented, a license determination is incomplete, the commercial invoice is insufficient, or the export filing was submitted too late.

    Operational definition: A compliant technology movement is a documented process that connects the item, parties, destination, authorization, transportation method, and delivery record before the shipment departs.

    This article provides a general framework for defense contracting and technology infrastructure deployments. It is not legal advice. Requirements may vary by item, destination, end user, contract, and transaction structure.

    1. Determine the regulatory status before movement

    The first step is to identify what is moving and why it is moving. A shipment may include hardware, software, technical data, services, replacement parts, tools, batteries, encryption features, or installation materials. Each category may have different regulatory treatment.

    The responsible organization should document:

    • The technical description and intended function of each item.
    • The manufacturer, model, serial number, and country of origin where applicable.
    • The end user, consignee, intermediate parties, and final destination.
    • Whether the item is being sold, transferred, repaired, loaned, returned, or temporarily exported.
    • Whether technical assistance or controlled information will be provided to personnel outside the United States.
    • The transportation route and method of movement.
    • The contract clauses and government direction applicable to the activity.

    A generic description such as “communications equipment” may not provide enough information for classification or customs review. Descriptions should be specific enough to support the applicable determination without disclosing sensitive operational information.

    The DFARS clause 252.225-7048 illustrates why export-control responsibilities must be addressed within government contracting workflows. Contracting officers, prime contractors, and subcontractors should identify who is responsible for classification, authorization, documentation, filing, and record retention.

    2. Apply OFAC controls to parties, destinations, and payments

    The Office of Foreign Assets Control administers U.S. economic sanctions programs. OFAC controls may apply to a transaction because of the destination, a party involved, a financial institution, a vessel or carrier, an ownership structure, or the nature of the activity.

    Quotable definition: OFAC screening is the process of evaluating relevant parties and transaction details against applicable sanctions restrictions before permitting a controlled transaction to proceed.

    OFAC analysis should not be limited to the equipment manufacturer or direct customer. A deployment may involve local vendors, freight forwarders, customs brokers, financial intermediaries, landlords, service providers, and other counterparties.

    A risk-based review should address:

    • The destination and any transit locations.
    • The end user and beneficial ownership of relevant entities.
    • Local suppliers, agents, and intermediaries.
    • Payment paths and financial institutions.
    • The goods, services, and technical support involved.
    • Any request to route the transaction through an unusual party or jurisdiction.

    OFAC’s A Framework for OFAC Compliance Commitments identifies management commitment, risk assessment, internal controls, testing and auditing, and training as core elements of a sanctions compliance program.

    For austere deployments, internal controls must remain usable when connectivity, staffing, and time are limited. Field personnel should have a clear process for stopping a questionable transaction and escalating it to the designated compliance or legal function. The process should also identify what records must be retained, including screening results, approvals, license determinations, and communications.
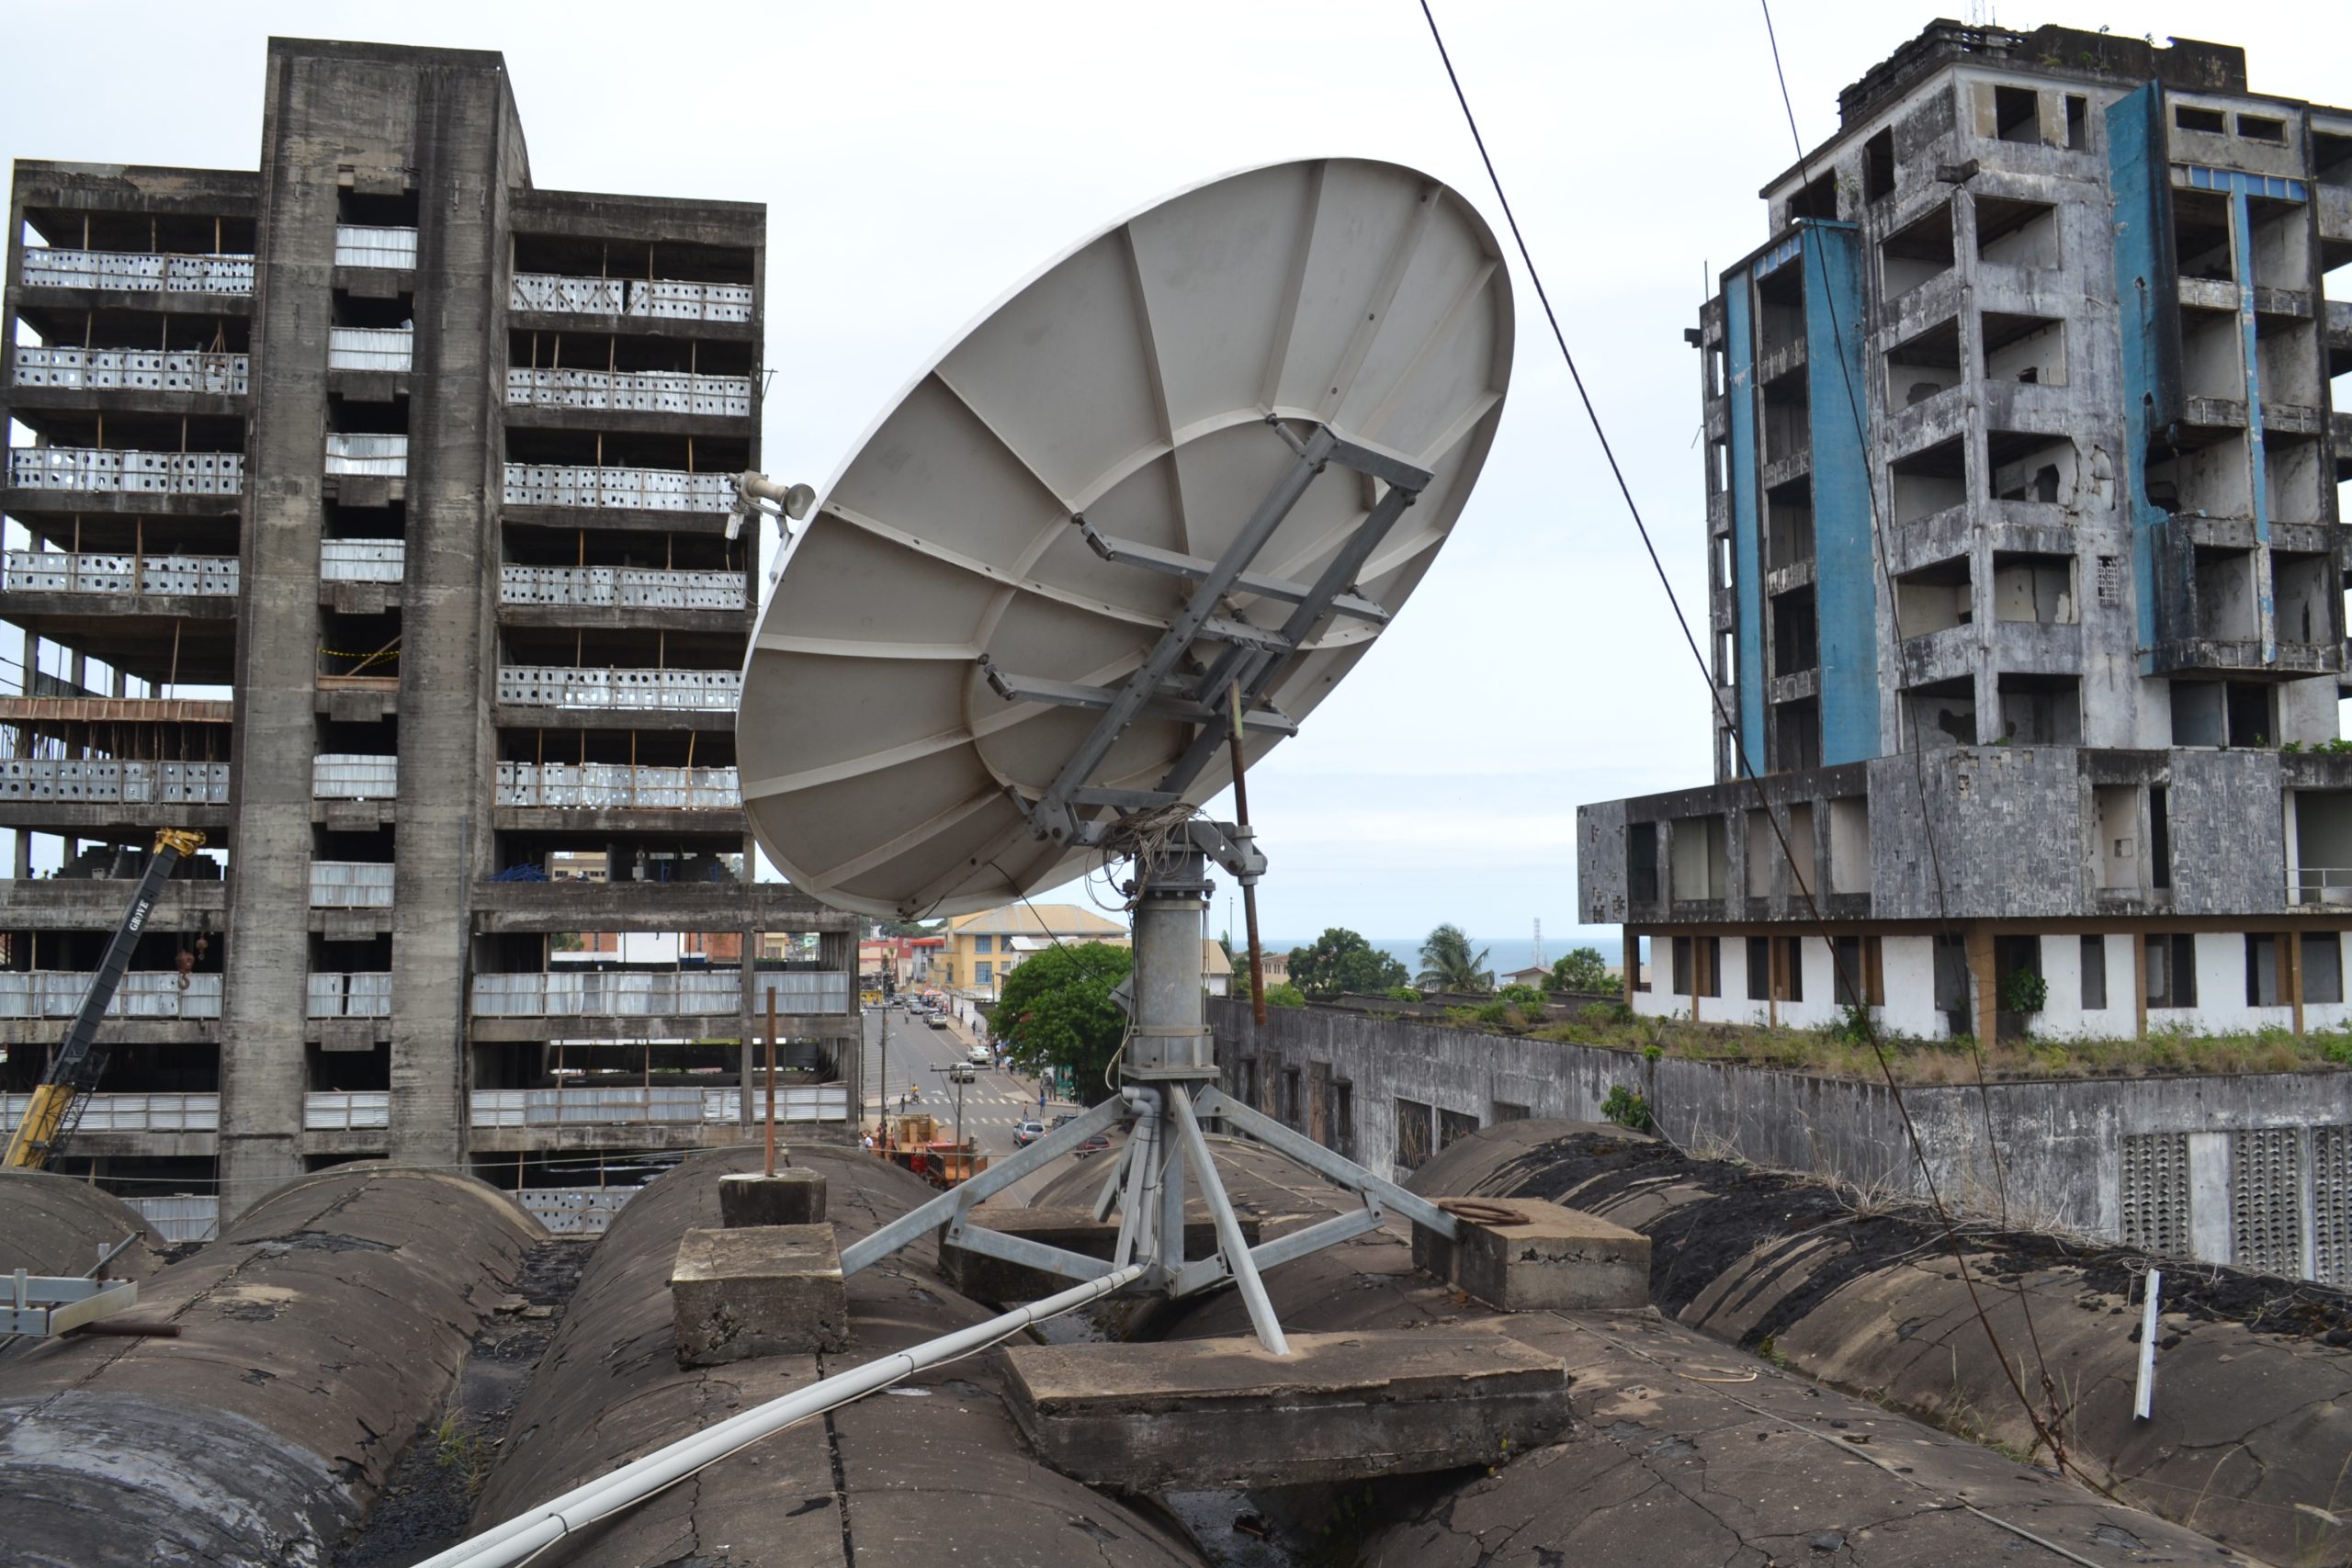
    Satellite communications equipment installed at an infrastructure-limited site

    3. Confirm whether ITAR authorization is required

    The International Traffic in Arms Regulations, or ITAR, govern defense articles, technical data, and defense services identified on the U.S. Munitions List. A technology deployment may implicate ITAR when it involves covered equipment, controlled technical data, or assistance related to a defense article.

    Quotable definition: ITAR authorization is the applicable license, exemption, or other approval that permits a qualifying export, temporary export, reexport, retransfer, or defense service under the circumstances presented.

    A temporary movement does not automatically avoid authorization requirements. Equipment that is expected to return to the United States may still require advance authorization unless a specific exemption applies.

    Government-directed activity may qualify for a narrow exemption under ITAR §126.4 in defined circumstances. However, a contractor should not assume that performance under a government contract, standing alone, creates an exemption. The organization should confirm:

    • Whether the item or information is subject to ITAR.
    • Whether the activity is an export, temporary export, reexport, retransfer, or defense service.
    • Whether a specific exemption applies.
    • Whether written government direction or other supporting documentation is required.
    • Whether the authorization covers the actual parties, destinations, quantities, and purpose.
    • Whether the equipment may be accessed by foreign persons during installation or support.
    • Whether records and post-shipment requirements apply.

    The current ITAR regulatory text is available through the Electronic Code of Federal Regulations. The regulation should be reviewed with the organization’s responsible export-control professional or legal counsel before movement.

    4. Prepare customs and export documentation

    Customs authorities require accurate information to determine admissibility, classification, valuation, origin, and applicable duties or restrictions. The documentation should be prepared before equipment reaches the port, airport, border, or receiving authority.

    For imports into the United States, the U.S. Customs and Border Protection importer guidance identifies the commercial invoice as a central document. Depending on the transaction, the invoice should include:

    • Seller, buyer, consignee, and importer information.
    • Invoice number and date.
    • Detailed descriptions of the goods.
    • Quantities and units of measure.
    • Unit values, total values, and currency.
    • Country of origin and country of export.
    • Terms of sale and applicable charges.
    • Information required by other government agencies where applicable.

    A pro forma invoice may be used for certain non-sale movements, such as temporary imports, repairs, samples, or returns. It should still contain enough information to support valuation, classification, and admissibility decisions.

    For exports from the United States, Electronic Export Information may be required through the Automated Export System. The requirement generally applies when the value of a Schedule B classification exceeds the applicable threshold or when the shipment is subject to export licensing or other filing requirements. The exporter or authorized filing agent should confirm the applicable rule rather than rely on a general low-value assumption.

    When EEI is accepted, the system issues an Internal Transaction Number. The Trade.gov AES filing guidance and Census AESDirect guidance explain how the filing and citation process works.

    The ITN or appropriate exemption citation should be provided to the carrier within the applicable pre-departure deadline. Timing may differ by vessel, air, truck, rail, or other transportation method. A shipment should not be tendered until the carrier has the required information.
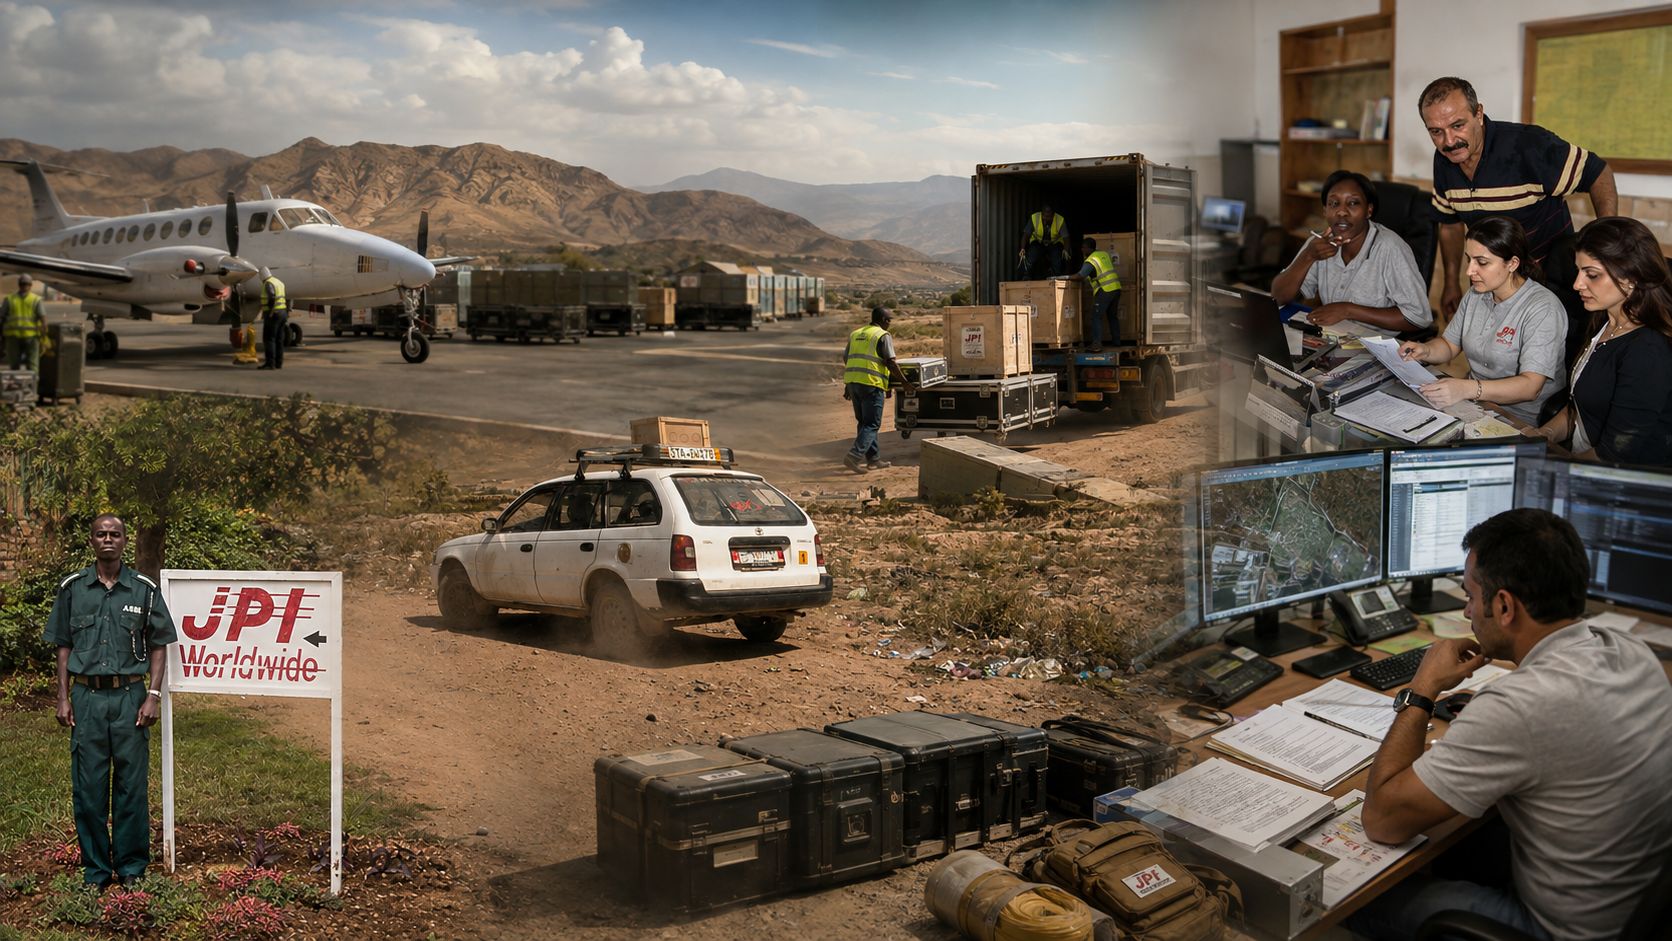
    Personnel and equipment coordinated for overseas field deployment

    5. Use a controlled pre-deployment workflow

    A practical workflow should connect compliance decisions to physical shipment preparation. The following sequence may reduce avoidable delays:

    1. Define the movement. Identify the items, technical data, services, parties, destination, route, and purpose.
    2. Classify the items. Determine the relevant customs and export-control classifications.
    3. Screen the parties. Review the customer, consignee, vendors, intermediaries, and financial parties as applicable.
    4. Confirm authorization. Determine whether a license, exemption, written direction, or other approval is required.
    5. Prepare the documents. Complete invoices, packing lists, transport documents, authorizations, and required statements.
    6. File required information. Submit EEI when required and obtain the ITN or applicable exemption citation.
    7. Validate the shipment. Confirm that the physical contents match the approved documents.
    8. Retain the record. Preserve approvals, filings, screening results, shipping records, and delivery confirmation according to applicable requirements.
    9. Control changes. Reassess the movement if the destination, consignee, routing, equipment, or end use changes.
    JPI technical personnel positioned for field deployment support

    6. How subcontractors can reduce friction for primes

    A subcontractor can reduce operational friction by making compliance-related information available before the prime contractor needs it. This includes accurate equipment lists, shipment values, technical descriptions, origin data, serial-number records, routing assumptions, personnel requirements, and proposed delivery schedules.

    JPI Worldwide supports government and prime-contractor teams with technology infrastructure, communications, cybersecurity, systems integration, technical staffing, logistics, and field deployment services. Its role may include procurement coordination, equipment staging, deployment planning, documentation support, transportation coordination, installation, commissioning, troubleshooting, and sustainment.

    These services do not replace the legal responsibilities of the exporter, importer, contracting party, or designated compliance function. They can, however, help connect technical readiness with movement planning so that avoidable documentation and coordination issues are identified earlier.

    7. Frequently asked questions

    Does an overseas government deployment automatically qualify for an exemption?

    No. Government involvement may be relevant to an exemption, but eligibility depends on the specific regulation and conditions. Written direction, official use, item status, parties, destination, and purpose may all matter.

    Is temporary equipment movement exempt from ITAR requirements?

    Not automatically. Temporary export status does not, by itself, eliminate the need for authorization. The equipment and activity must be reviewed under the applicable rules.

    Is an OFAC check the same as an ITAR review?

    No. OFAC addresses sanctions-related restrictions involving parties, jurisdictions, transactions, and other designated interests. ITAR addresses defense articles, technical data, and defense services. The reviews may overlap, but one does not replace the other.

    Who is responsible for customs accuracy?

    Responsibility may be allocated by the transaction and contract structure. The importer, exporter, principal party in interest, authorized agent, broker, carrier, and other parties may have defined responsibilities. Those roles should be documented before shipment.

    How can a subcontractor support a prime contractor?

    A subcontractor may support the prime by providing accurate technical and logistics information, maintaining shipment records, coordinating field personnel, and escalating changes or compliance questions before movement. The subcontractor should not make unsupported legal assumptions on behalf of the prime.

    8. Administrative limitations and contact

    Regulatory requirements may change. Country-specific sanctions, customs procedures, contract clauses, licensing conditions, and host-nation requirements may impose additional obligations. Information in this article is provided for general informational purposes and should not be treated as a legal determination or authorization to export, import, reexport, retransfer, or provide services.

    JPI Worldwide can discuss how its communications, technology infrastructure, cybersecurity, technical staffing, logistics, and field deployment capabilities may support a government agency, prime contractor, or subcontractor. To discuss a requirement, use the JPI Worldwide contact page, email connect@jpiworldwide.com, or call +1-509-210-3023.

    Do not submit classified information, Controlled Unclassified Information, export-controlled technical data, passwords, credentials, or other sensitive material through a public contact form.

    Authoritative references

  • What Primes Really Expect From a Subcontractor: Compliance, Accounting, and Friction

    What Primes Really Expect From a Subcontractor: Compliance, Accounting, and Friction

    Page label: Government Contracting Insights
    Revision date: August 31, 2026
    Author: Penny Marbel (JPI Worldwide)

    A first-time subcontractor may assume that technical capability is the primary requirement for entering defense contracting.
    Technical capability is necessary, but it is not sufficient.

    Prime contractors also evaluate whether a subcontractor can perform consistently, document its work, support accurate billing, comply with applicable contract requirements, and communicate risks before they affect delivery. These factors determine whether a subcontractor reduces operational friction or creates additional management exposure.

    A prime-ready subcontractor is a company that can perform the assigned work, support its costs, comply with applicable flow-down requirements, and provide the records needed for responsible contract administration.

    This standard applies to companies of different sizes and specialties. A business does not need to provide every government contracting service. It must identify a defensible niche and operate that niche with discipline.

    1. What does a prime contractor expect from a subcontractor?

    A prime contractor generally expects a subcontractor to satisfy five conditions:

    • Perform the required technical work.
    • Maintain adequate business and accounting controls.
    • Accept and comply with applicable subcontract terms.
    • Provide complete and timely documentation.
    • Identify performance, cost, staffing, and schedule risks early.

    The prime remains responsible for managing its government contract. Under FAR Part 44, the prime may need to evaluate subcontractor responsibility, technical justification, pricing, financial capability, and contract compliance.

    This does not mean that every subcontractor must maintain the same systems as a large defense contractor. Requirements depend on the contract type, applicable clauses, dollar value, nature of the work, and terms flowed down by the prime.

    However, a subcontractor should be able to demonstrate that its internal practices are proportionate to the work being performed.

    2. Why does compliance matter to the prime?

    Compliance matters because the prime’s risk does not end at the prime contract boundary.

    A subcontractor may be responsible for a specific technical deliverable, labor category, installation activity, or logistics function. The prime must still determine whether the subcontractor can perform the work and whether the subcontractor’s costs and performance can be supported if reviewed.

    Applicable requirements may include:

    • Contract-specific technical and quality requirements.
    • Labor, safety, timekeeping, and recordkeeping obligations.
    • Restrictions on subcontracting and assignment.
    • Cybersecurity and information-handling requirements.
    • Domestic sourcing or supply-chain provisions.
    • Pricing and cost-data requirements.
    • Audit-access and records-retention provisions.
    • Applicable FAR, DFARS, agency, and contract clauses.

    A subcontractor should not assume that a clause applies merely because it appears in a government contract. Flow-down requirements must be reviewed against the actual prime contract and subcontract. At the same time, a subcontractor should not assume that a requirement is irrelevant because the company does not contract directly with the government.

    The correct approach is to maintain a controlled process for reviewing the subcontract, identifying applicable requirements, assigning internal responsibility, and retaining evidence of compliance.

    3. What accounting controls do primes look for?

    Primes expect accounting records to show what work was performed, for which contract or task, during which period, and at what cost.

    Under FAR 31.201-2, a cost is allowable only when it satisfies requirements relating to reasonableness, allocability, applicable accounting standards, contract terms, and stated cost limitations. The same section requires contractors to maintain records and supporting documentation adequate to demonstrate that claimed costs were incurred, allocable, and allowable.

    For a subcontractor, practical accounting controls may include:

    • Separating direct contract costs from indirect costs.
    • Assigning labor and material costs to the correct contract or task.
    • Maintaining consistent indirect-cost allocation practices.
    • Retaining invoices, receipts, purchase records, and approvals.
    • Reconciling billed amounts to the general ledger.
    • Tracking subcontractor and supplier costs separately.
    • Recording labor against authorized projects and labor categories.
    • Identifying unallowable costs before they enter an invoice or proposal.
    • Preserving records for the period required by the subcontract.

    The objective is not to create unnecessary administrative complexity. The objective is traceability.

    A prime should not have to reconstruct how an invoice was prepared. A well-supported invoice allows the prime to review the amount, compare it to the subcontract terms, and incorporate it into its own billing or reporting process.

    JPI Worldwide technical personnel working with network equipment in a generic operations room

    4. What is the difference between direct, indirect, and unallowable costs?

    Direct costs are costs that can be identified specifically with a contract or other final cost objective.

    Indirect costs benefit multiple contracts or business activities and are allocated using a reasonable and consistently applied method.

    Unallowable costs are costs that may not be included in a government contract billing, claim, or proposal under applicable law, regulation, or contract terms.

    The classification must be applied consistently. A company should not treat the same type of cost as direct in one situation and indirect in another without a documented business reason.

    Examples that may require additional review include:

    • Travel that lacks the required business purpose and destination records.
    • Materials purchased without a connection to the contract requirement.
    • Labor charged to the wrong project or period.
    • Personal expenses included with business expenses.
    • Costs prohibited by FAR Part 31.
    • Costs associated with activities that are not within the subcontract scope.
    • Indirect expenses allocated using a base that does not reflect the benefit received.

    Under FAR 31.201-6, expressly unallowable costs and directly associated costs must be identified and excluded from government contract billings, claims, and proposals.

    A subcontractor should establish an invoice review process before the first invoice is submitted. Corrections are more manageable when identified internally rather than after the prime or an auditor raises a question.

    5. Why do primes ask for pricing support?

    Prime contractors must establish that subcontract prices are fair and reasonable. Under FAR 15.404-3, primes and higher-tier subcontractors must conduct appropriate cost or price analyses of proposed subcontract prices and include the results in their own proposals when required.

    A first-time subcontractor may therefore be asked for more than a total price. The prime may request:

    • Labor categories and proposed labor rates.
    • Estimated labor hours.
    • Material and equipment costs.
    • Travel and other direct costs.
    • Indirect rates and allocation bases.
    • Basis-of-estimate documentation.
    • Historical pricing or market support.
    • Commerciality information, where applicable.
    • Certified cost or pricing data, when required.
    • Assumptions, exclusions, and schedule constraints.

    Price analysis examines whether the total proposed price is reasonable. Cost analysis examines individual cost elements and profit or fee. The appropriate method depends on the circumstances and applicable requirements.

    A subcontractor should provide clear assumptions and avoid unsupported precision. If labor hours depend on site access, equipment availability, customer-furnished property, or other conditions, those dependencies should be stated in the proposal.

    Incomplete pricing support can delay negotiations. It may also cause the prime to select a different source even when the subcontractor has the required technical skill.

    6. What does “low friction” mean in government contracting?

    Low friction means that the prime can integrate the subcontractor into its program without repeated clarification, correction, or administrative escalation.

    A low-friction subcontractor:

    • Responds to requests within agreed timeframes.
    • Provides complete proposal and invoice packages.
    • Uses the required labor categories and billing structure.
    • Maintains current points of contact.
    • Reports schedule or staffing risks promptly.
    • Documents technical completion and acceptance.
    • Controls subcontractor and supplier relationships.
    • Protects contract and operational information.
    • Separates facts, assumptions, and unresolved issues.
    • Maintains an orderly records package.

    Low friction does not mean that a subcontractor reports no problems. It means that problems are identified early, described accurately, and accompanied by a practical corrective path.

    A prime contractor generally has more confidence in a subcontractor that reports a manageable issue promptly than in one that delays disclosure until the issue affects delivery.

    Modular technical facilities in an industrial operating environment

    7. Can a small or first-time company find a niche in defense contracting?

    Yes. A company does not need to become a full-service defense contractor to participate in government contracting.

    A viable niche may involve:

    • Network installation and structured cabling.
    • Communications equipment integration.
    • Cybersecurity implementation support.
    • Technical staffing and field service.
    • Equipment staging and deployment logistics.
    • Help desk or systems administration.
    • Data-center or machine-room support.
    • AI workflow and systems integration.
    • Testing, commissioning, and maintenance.
    • Specialized engineering or technical consulting.

    The relevant question is not whether a company can perform every requirement. The relevant question is whether the company can define a specific service, demonstrate competence, support its pricing, and meet the administrative requirements attached to that service.

    JPI Worldwide’s government capabilities and integrated technology capabilities illustrate how specialized services can be organized into a subcontractor offering. Communications, infrastructure, cybersecurity, systems integration, technical staffing, logistics, and field support may be provided as distinct capabilities or coordinated components of a larger requirement.

    8. Prime-ready subcontractor checklist

    Before pursuing a subcontract, a first-time government contractor should confirm that it can:

    • Describe its technical niche in one clear paragraph.
    • Identify the labor, equipment, and deliverables it will provide.
    • Explain how direct and indirect costs are recorded.
    • Produce an invoice tied to the subcontract terms.
    • Support proposed labor rates and material costs.
    • Maintain timekeeping and project records.
    • Review applicable FAR, DFARS, and agency flow-down clauses.
    • Protect contract information and avoid submitting sensitive information through unsecured channels.
    • Provide evidence of financial and operational capacity.
    • Identify a responsible contract administrator and technical point of contact.
    • Report risks before they become missed milestones.
    • Retain records in an organized and retrievable form.

    This checklist is a starting point. Contract-specific requirements may impose additional obligations.

    9. How can JPI Worldwide support a prime or subcontractor team?

    JPI Worldwide operates as a technology and field-support subcontractor for government programs, prime contractors, subcontractors, and mission partners. Its capabilities include network engineering, communications infrastructure, cybersecurity, AI and systems integration, technical staffing, logistics, deployment coordination, and sustainment.

    JPI’s role may be structured around a focused technical requirement or a broader field-support effort. The appropriate scope depends on the prime contract, subcontract terms, technical requirements, schedule, operating environment, and applicable compliance obligations.

    A business, agency, department, or contractor team seeking a reliable technical subcontractor may contact JPI Worldwide to discuss the requirement. Information submitted through the public contact form should not include classified information, Controlled Unclassified Information, export-controlled technical data, passwords, credentials, or other sensitive material.

    JPI Worldwide can discuss how its capabilities may help reduce operational friction, strengthen field execution, and support a prime contractor’s delivery obligations.

    Administrative notice

    This article is provided for informational purposes. It does not constitute legal, accounting, audit, or contracting advice. FAR, DFARS, agency supplements, and subcontract terms may change or may apply differently based on contract type, agency, dollar value, and performance requirements. Contract-specific questions should be reviewed with qualified counsel, accounting professionals, or the responsible contracting officials.

    Sources

  • 7 Mistakes Government Contractors Make with Cybersecurity at the Tactical Edge

    7 Mistakes Government Contractors Make with Cybersecurity at the Tactical Edge

    Page: Government Contracting Insights
    Revision date: August 31, 2026

    Government contractors operating at the tactical edge face cybersecurity conditions that differ from those found in a conventional enterprise environment. Connectivity may be intermittent. Equipment may be staged rapidly. Personnel may rotate. Technical support may be limited. Systems may need to operate across fixed facilities, temporary sites, remote offices, and contractor-managed networks.

    These conditions increase the consequences of basic cybersecurity errors.

    For government agencies and prime contractors, the issue is not limited to whether a subcontractor can install a firewall or configure a virtual private network. The more important question is whether the supporting organization can implement, document, monitor, and sustain security controls within the actual operating environment.

    Tactical-edge cybersecurity is the continuous protection of networks, systems, users, and operational data where infrastructure, connectivity, personnel, and support resources may be constrained.

    The following seven mistakes frequently create avoidable risk and operational friction for government contractors.

    1. Treating compliance as a one-time project

    Cybersecurity compliance is not complete when an assessment package is submitted or a contract requirement is reviewed.

    NIST SP 800-171 Rev. 3 describes security requirements for protecting Controlled Unclassified Information in nonfederal systems and organizations. The requirements apply to system components that process, store, or transmit CUI, as well as components that protect those systems. Contract clauses and agency direction determine how specific requirements apply to a particular effort.

    A common mistake is to treat the security plan, policies, assessment results, and remediation records as static documents. Tactical deployments make this approach unreliable. A change in network architecture, equipment, cloud service, user population, or data flow may change the applicable risk profile.

    Government contractors should:

    • Assign an owner for each applicable control.
    • Review security documentation after material system changes.
    • Maintain current system security plans and remediation records.
    • Monitor authentication, configuration, vulnerability, and access events.
    • Validate that controls continue to operate after deployment.

    A prime contractor should be able to determine whether a subcontractor’s security posture is being maintained during performance, not only whether documentation existed at contract award.

    2. Failing to define the CUI and FCI boundary

    A security boundary identifies the systems, users, devices, applications, services, and data flows included in a protection requirement. Without a defensible boundary, the contractor may protect too much, protect too little, or be unable to explain the scope of its security program.

    Federal Contract Information and CUI should not be treated as interchangeable terms. Their handling requirements depend on the contract, applicable clauses, agency direction, and the nature of the information.

    The boundary should account for:

    • Email and collaboration platforms.
    • File shares and removable media.
    • Endpoints and privileged workstations.
    • Cloud services and hosted applications.
    • Remote-access systems and VPN infrastructure.
    • Network devices, logging systems, and administrative tools.
    • Contractor and subcontractor data exchanges.

    A practical data-flow review should answer four questions:

    1. What information is being received?
    2. Where is the information stored?
    3. Which users and systems can access it?
    4. How is the information transmitted, backed up, and removed?

    If these questions cannot be answered with reasonable precision, the environment is not yet adequately scoped.

    Diagram showing a segmented tactical-edge network with a firewall, user network, administration network, and protected CUI enclave

    3. Allowing weak identity and access controls

    Identity controls are often the first technical barrier between an exposed service and an unauthorized user. CISA and NSA guidance identifies weak or misconfigured multifactor authentication, excessive privileges, poor credential hygiene, and default credentials as recurring weaknesses.

    At the tactical edge, access may be required by rotating personnel, remote administrators, local technical staff, and multiple contractor organizations. That complexity does not eliminate the requirement for controlled access. It makes access governance more important.

    Government contractors should:

    • Require multifactor authentication for remote access, external-facing services, and privileged accounts.
    • Use phishing-resistant MFA for sensitive systems where supported.
    • Separate administrative and standard user accounts.
    • Apply least privilege to users, service accounts, and machine accounts.
    • Remove inactive and unnecessary accounts.
    • Change vendor-supplied usernames and passwords before production use.
    • Review access after personnel transfers, rotations, and departures.

    Access should be granted based on an approved operational need. Convenience should not be used as a substitute for authorization.

    4. Deploying systems without secure configuration and patch discipline

    Rapid deployment can create pressure to use factory settings, defer hardening, or connect equipment before configuration validation is complete. This is a significant risk.

    The 2023 joint NSA and CISA advisory on common cybersecurity misconfigurations identifies default configurations, poor patch management, insufficient segmentation, and weak access controls among the most common problems observed across assessed environments.

    A secure deployment process should include:

    • Asset identification and inventory.
    • Configuration baselines for operating systems, applications, firewalls, and network devices.
    • Removal or disabling of unused services.
    • Elimination of default credentials.
    • Risk-based patching of software, firmware, and operating systems.
    • Prioritization of vulnerabilities listed in CISA’s Known Exploited Vulnerabilities Catalog.
    • Documentation of exceptions where patching is not immediately feasible.
    • Compensating controls, such as segmentation, where legacy systems must remain in service.

    Unsupported hardware and software require particular attention. If replacement is not immediately possible, the risk should be documented and reduced through isolation, restricted access, monitoring, and a defined replacement plan.

    5. Assuming connectivity is security

    A network can be available and still be insecure. Connectivity establishes a path for communications. It does not establish trust.

    A tactical-edge environment may combine commercial internet access, wireless links, satellite connectivity, local networks, remote-access services, and temporary equipment. Each connection can introduce a separate configuration and monitoring requirement.

    Network segmentation reduces the ability of an intruder to move from one compromised system to another. At a minimum, contractors should evaluate separation among:

    • User devices.
    • Administrative workstations.
    • Network-management interfaces.
    • Servers and applications.
    • Sensitive-data environments.
    • Operational technology or specialized equipment.

    Segmentation should be enforced through properly configured firewalls, VLANs, access-control lists, application-aware controls, and restricted management paths. A network diagram should reflect the deployed architecture rather than an outdated design concept.

    JPI Worldwide’s network engineering and cybersecurity capabilities include secure architecture, network segmentation, firewall and access-control implementation, secure remote access, system hardening, monitoring, and support for remote and field systems.

    Technical personnel working around network racks and monitoring systems in a controlled operations room

    6. Operating without centralized monitoring and rehearsed response procedures

    A contractor may have security tools installed and still lack meaningful visibility. Logs that remain on individual devices may be difficult to correlate. Alerts may not have an assigned owner. Incident procedures may exist but have never been exercised.

    CISA recommends centralized log management, detection tools, secure configurations, and updated software as foundational practices. NSA and CISA also recommend validating security controls against known adversary techniques.

    A practical monitoring and response capability should define:

    • Which systems generate logs.
    • Where logs are collected and retained.
    • Which events require notification.
    • Who reviews alerts.
    • How incidents are escalated.
    • Which contractual reporting obligations apply.
    • How evidence is preserved.
    • How recovery and operational continuity are managed.

    Incident response procedures should address degraded connectivity and limited local support. A field team may not have the same resources as a headquarters security operations center. The response model should account for that limitation before an incident occurs.

    7. Maintaining inadequate evidence of control operation

    A policy can describe an intended practice. Evidence demonstrates whether that practice was implemented and operated.

    For a government contractor, a useful body of evidence may include:

    • Approved policies and procedures.
    • System security plans.
    • Network diagrams and data-flow maps.
    • Configuration baselines.
    • Access reviews.
    • Vulnerability and patch records.
    • Security training records.
    • Log-retention and monitoring records.
    • Incident response exercises.
    • Remediation plans and closure documentation.
    • Change-management records.

    Evidence should be current, attributable, and connected to the applicable system. Screenshots without context, undated spreadsheets, and generic policy documents may not establish that a control operated during the relevant performance period.

    Contractors must also ensure that representations concerning cybersecurity status are accurate and supported. The applicable contract, DFARS provisions, agency instructions, and other governing requirements should be reviewed with qualified legal and compliance personnel where necessary.

    Prime and contracting officer review component

    Before relying on a subcontractor’s cybersecurity capability, a prime contractor or contracting officer should confirm that the supporting organization can answer the following questions:

    • What systems and data are within the security boundary?
    • Who owns each security control?
    • How are remote and privileged users authenticated?
    • How are deployed systems hardened before connection?
    • How are patches and exceptions tracked?
    • Where are security logs collected and reviewed?
    • What is the incident escalation process?
    • What evidence demonstrates that controls are operating?
    • How will security responsibilities be coordinated across the prime and subcontractor teams?

    These questions are not intended to replace a formal assessment. They provide an operational screen for identifying preventable gaps before those gaps affect schedule, performance, data protection, or contract administration.

    How JPI Worldwide can reduce operational friction

    JPI Worldwide supports government agencies, prime contractors, and subcontractor teams with cybersecurity, networking, communications, systems integration, technical staffing, deployment, and sustainment services. Its work can extend from secure architecture and configuration review to field installation, troubleshooting, monitoring support, training, and operational handoff.

    For primes, the value of a capable subcontractor is not limited to technical labor. The subcontractor should integrate into the program’s reporting, change-control, security, logistics, and performance-management processes without creating unnecessary coordination burdens.

    JPI supports government and prime-contractor requirements in CONUS and OCONUS environments. Its experience includes communications, network infrastructure, field operations, technical personnel, logistics, and sustained support in environments where infrastructure and access may be constrained.

    Organizations evaluating cybersecurity services for a government program, field deployment, or subcontracting requirement may contact JPI Worldwide to discuss the business, agency, or department requirement. Do not submit classified information, CUI, export-controlled technical data, passwords, credentials, or other sensitive material through the public contact form.

    Sources and further reading

    The cited requirements and guidance may change. Contract-specific obligations control where they differ from general educational material. This article is provided for informational purposes and does not constitute legal, regulatory, or contracting advice.

  • 5 Steps to Deploy Secure Network Infrastructure in an OCONUS War Zone

    5 Steps to Deploy Secure Network Infrastructure in an OCONUS War Zone

    Page: Field Guide for Prime Contractors
    Revision date: August 31, 2026

    A secure network deployment in an OCONUS conflict-affected environment requires more than equipment delivery and initial connectivity. The system must support mission requirements, protect information, tolerate disrupted infrastructure, and remain supportable after installation.

    For prime contractors, the subcontractor’s value is measured by more than technical capability. It is also measured by planning discipline, documentation, logistics coordination, configuration control, and the ability to resolve field issues without creating additional program friction.

    Definition: Secure network infrastructure is an integrated combination of communications paths, network equipment, security controls, personnel, procedures, and sustainment resources designed to provide authorized connectivity while limiting unauthorized access and operational disruption.

    The following five steps provide a practical framework for planning and executing network deployment services and tactical communications support in remote or high-risk operating environments.

    1. Define the Mission Before Selecting the Technology

    A network should be designed around approved mission requirements. Technology selection should follow the mission, not determine it.

    What should be documented first?

    Before equipment is procured or configured, the prime and its technical partners should document:

    • Required users and authorized user groups.
    • Applications and services that must be available.
    • Data sensitivity and handling requirements.
    • Required availability and recovery objectives.
    • Expected power, environmental, and physical constraints.
    • Approved communications paths and dependencies.
    • Support responsibilities after commissioning.
    • Contractual, agency, and security requirements.

    This information should be captured in a controlled requirements document. The document should identify assumptions that require customer approval. It should also distinguish mandatory capabilities from preferred features.

    The mission analysis should not disclose sensitive operational details in general project documentation. Specific locations, facility names, movement schedules, force information, and security procedures should be handled through approved channels and access controls.

    Why does this reduce risk for primes?

    Unclear requirements create downstream changes. Those changes may affect the bill of materials, shipping plan, configuration baseline, staffing model, schedule, and authorization process.

    A prime contractor can reduce avoidable friction by requiring a clear decision record before deployment. The record should establish who owns each requirement and which conditions require an engineering change, customer approval, or contract modification.

    NIST Special Publication 800-207 provides a useful foundation for treating applications, services, devices, and data as protected resources rather than assuming that a network location is trusted. Its guidance should be adapted to the specific agency and contract environment.

    2. Design for Multiple Transport Options

    OCONUS networks should not depend on a single communications path unless the mission specifically permits that limitation.

    Definition: Tactical communications are communications capabilities designed to support authorized users and mission systems where infrastructure, access, bandwidth, power, or connectivity may be constrained or subject to disruption.

    A deployment may use a combination of fiber, wired Ethernet, wireless backhaul, commercial broadband, radio, and satellite connectivity. Satellite communications may be appropriate in some environments, but it should be treated as one component of a broader communications architecture rather than the default solution for every requirement.

    How should transport diversity be evaluated?

    Each available path should be evaluated against:

    • Availability and expected outage conditions.
    • Bandwidth and latency requirements.
    • Authentication and encryption capabilities.
    • Physical installation constraints.
    • Power consumption and environmental tolerance.
    • Local regulatory and customs requirements.
    • Maintenance and replacement requirements.
    • Dependency on commercial or third-party services.

    The design should identify which services can operate over each path and which services require a specific level of performance. It should also define failover behavior. A backup path that has not been tested under realistic conditions should not be treated as an operational capability.

    A resilient design may use different paths for different purposes. For example, essential management traffic may require a protected low-bandwidth path, while bulk data may use a higher-bandwidth connection when available. The architecture should specify those priorities in advance.

    JPI Worldwide describes its communications capabilities as including wired, wireless, radio, broadband, and remote connectivity options. Its network engineering and infrastructure capabilities also include routing, switching, fiber infrastructure, monitoring, redundancy, and field installation.

    Five-layer architecture for secure OCONUS network deployment

    3. Segment the Network and Enforce Access

    A secure network should not operate as one undifferentiated trusted zone.

    The design should separate mission systems, user services, administration, equipment management, and other approved traffic categories according to the applicable security and operational requirements.

    What does segmentation accomplish?

    Segmentation limits unnecessary communication between systems. It can reduce lateral movement if an account, device, or service is compromised. It also makes monitoring and troubleshooting more manageable.

    At a minimum, the architecture should consider separate controls for:

    • Mission applications and mission data.
    • General user access.
    • Network and device management.
    • Contractor support activity.
    • Guest or partner connectivity.
    • Infrastructure services such as DNS, authentication, and logging.

    Access between segments should be explicitly authorized. Default-deny policies should be considered where operationally appropriate. Rules should identify the source, destination, service, purpose, and responsible owner.

    NIST SP 800-207 describes a zero trust architecture in which access is evaluated through policy and enforcement components. The model includes a Policy Engine, a Policy Administrator, and Policy Enforcement Points. In a field deployment, enforcement may be implemented through firewalls, gateways, routers, secure access systems, or other approved controls.

    Zero trust does not mean that every field system must use an identical product or topology. It means that access should not be granted solely because a user or device is connected to an internal network.

    What should be verified?

    The prime and its technical subcontractor should verify:

    • User identity and role.
    • Device identity and security posture.
    • Application or service authorization.
    • Data sensitivity.
    • Session duration and privilege level.
    • Logging and alerting requirements.
    • Revocation procedures for personnel, devices, and credentials.

    The applicable contract, agency policy, system security plan, authorization boundary, and security control baseline remain controlling. NIST guidance is not a substitute for those requirements.

    4. Stage, Harden, and Validate Before Deployment

    Equipment should be staged and tested before it is moved into an austere environment.

    Definition: Configuration control is the documented process used to establish, approve, track, test, and maintain the hardware, software, firmware, and security settings that make up an operational system.

    Pre-deployment staging should include a controlled bill of materials, approved configuration baseline, device inventory, labeling scheme, test plan, and documentation package. Hardware should be inspected before shipment. Software and firmware versions should be recorded according to program requirements.

    What should a pre-deployment test include?

    The test plan should address:

    • Device startup and recovery.
    • Network addressing and routing.
    • Segmentation and access-control rules.
    • Authentication and administrative access.
    • Encryption and certificate operation.
    • Monitoring, logging, and alert generation.
    • Failover and restoration procedures.
    • Equipment interoperability.
    • Power and environmental considerations.
    • End-to-end service validation.

    Test results should identify the test condition, expected result, actual result, responsible technician, date, and disposition of any exception. Open defects should have an owner and resolution path before shipment unless the customer has approved a documented exception.

    This process helps the prime demonstrate that a problem discovered in the field is a site condition rather than an avoidable configuration error. It also supports contract administration, acceptance testing, warranty coordination, and future troubleshooting.

    JPI’s government capabilities include procurement, configuration, integration, installation, testing, troubleshooting, technical staffing, and deployment support. Those functions can be coordinated as part of a larger prime-contractor delivery model.

    JPI Worldwide technician validating network equipment inside a rugged technical room

    5. Plan for Sustainment, Compliance, and Operational Handoff

    Deployment is not complete when equipment is powered on. The system must be supportable throughout the period of performance.

    What belongs in the sustainment plan?

    A sustainment plan should address:

    • Preventive and corrective maintenance.
    • Spare equipment and consumables.
    • Configuration backup and restoration.
    • Patch and vulnerability management.
    • Credential and certificate lifecycle management.
    • Monitoring and escalation procedures.
    • Personnel rotations and knowledge transfer.
    • Replacement equipment and resupply.
    • Incident response coordination.
    • End-of-life and equipment disposition.

    The plan should define the boundaries between the prime, subcontractor, government customer, service providers, and local support personnel. It should also identify the records required for acceptance, recurring reporting, security review, and contract closeout.

    Where systems handle CUI or covered defense information, the team must follow the applicable contract clauses and agency requirements. For DoD work, DFARS 252.204-7012 may impose safeguarding, cyber incident reporting, preservation, and cooperation obligations. The current contract language and authorized security personnel should be consulted before project execution.

    Personnel should not transmit classified information, CUI, export-controlled technical data, credentials, or other sensitive material through a public contact form or ordinary email. JPI’s contact page specifically directs visitors not to submit such information through its public form.

    Operational readiness cycle for planning, staging, validating, and sustaining a deployed network

    Frequently Asked Questions

    What is the most important first step in an OCONUS network deployment?

    The first step is to establish and approve mission requirements. Equipment selection should follow documented user, application, security, availability, power, environmental, and support requirements.

    Is satellite communications required for every OCONUS deployment?

    No. Satellite communications may be appropriate where terrestrial infrastructure is unavailable or unreliable, but the correct solution depends on the mission, available transport, regulatory conditions, bandwidth, latency, resilience, and sustainment model.

    How does zero trust apply to a field network?

    Zero trust requires explicit, policy-based decisions for users, devices, applications, and data. Network location alone should not establish trust. Authentication, authorization, segmentation, encryption, monitoring, and revocation should be incorporated into the architecture.

    Why should primes use a specialized network deployment subcontractor?

    A specialized subcontractor may reduce coordination burden by combining engineering, equipment staging, field installation, logistics, testing, troubleshooting, and sustainment support. The exact scope should be defined by the statement of work, technical requirements, and approved responsibilities.

    Conclusion

    Secure network infrastructure in an OCONUS conflict-affected environment depends on disciplined execution. The five essential steps are:

    1. Define the mission and constraints.
    2. Design for transport diversity.
    3. Segment the network and enforce access.
    4. Stage, harden, and validate before deployment.
    5. Plan for sustainment and operational handoff.

    JPI Worldwide supports government agencies, prime contractors, subcontractors, and mission partners with network infrastructure, tactical communications, cybersecurity, technical staffing, logistics, and field deployment services. Contact JPI Worldwide to discuss how JPI may support a business, agency, department, program, or overseas deployment requirement.

    Authoritative References

  • Civilian Contractors in Latin America: The Infrastructure Behind U.S. Mission Support

    Civilian Contractors in Latin America: The Infrastructure Behind U.S. Mission Support

    When most people think about U.S. government activity in Latin America and the Caribbean, they picture diplomats, military personnel, law-enforcement agencies, or humanitarian missions. Less visible—but often essential—is the civilian contractor workforce that provides the technology, communications, logistics, infrastructure, maintenance, staffing, and sustainment required to keep those missions operating.

    This is not an unusual exception to federal operations overseas. It is built into the U.S. acquisition framework.

    The Federal Acquisition Regulation expressly addresses contractor personnel working in designated operational areas and supporting diplomatic or consular missions outside the United States. FAR 52.225-19 states plainly that “Contractor personnel are civilians.” It also anticipates contractor support during contingency operations, humanitarian or peacekeeping operations, other military operations, exercises, and certain diplomatic missions. [1]

    For companies supporting U.S. government missions in the Western Hemisphere, the practical implication is significant: mission success often depends on a civilian support structure operating alongside—not as part of—the military or diplomatic workforce.

    SOUTHCOM’s Area of Responsibility

    U.S. Southern Command, or SOUTHCOM, is responsible for U.S. military activity across Central America, South America, and the Caribbean, with limited territorial exceptions. SOUTHCOM also has responsibility for the protection of U.S. military resources in the region and for defense of the Panama Canal. [2]

    The command’s current priorities extend well beyond traditional military operations. SOUTHCOM identifies missions involving:

    • command and control;
    • counter-narcotics and counter-cartel activity;
    • cybersecurity and space defense;
    • security cooperation;
    • humanitarian and disaster relief;
    • infrastructure;
    • logistics and sustainment;
    • modernization; and
    • cooperation with regional partners. [3]

    SOUTHCOM describes its regional approach as working “by, with, and through” partner nations. That operating model creates substantial requirements for communications, interoperability, logistics, technology deployment, maintenance, training, and technical support. [4]

    Those requirements do not disappear because a mission is outside a traditional combat zone. In many cases, geography makes support more complicated.

    A project in Central America, the Caribbean, the Andes, or a remote part of South America may need reliable communications where terrestrial infrastructure is limited; equipment that must clear customs and travel hundreds of miles; personnel who can deploy and operate independently; redundant power and connectivity; local coordination; cybersecurity; and technical support after installation.

    That is the environment in which civilian mission-support contractors become important.

    Haiti Shows What Mission Support Looks Like in Practice

    Recent U.S. support to Haiti provides a concrete example.

    In 2024, the State Department described more than $200 million in Department of Defense funding for construction and operation of the logistics support area used in support of the Multinational Security Support mission in Haiti. State Department officials specifically noted that the funding went to contractors that constructed and operated the base. [5]

    A subsequent U.S. government report to Congress provides more detail about what this contractor-supported infrastructure actually included. DoD sustainment contracts for the Logistics Support Area at Toussaint Louverture International Airport provided food, sanitation, billeting capacity for up to 1,000 personnel, vehicle maintenance, mission-planning space, and other operational requirements. [6]

    That example is useful because it illustrates what “government contracting overseas” often means in operational terms.

    It is not necessarily a weapons program or a large weapons platform.

    It may be:

    communications + facilities + transportation + maintenance + IT + personnel + logistics + sustainment.

    All of those functions have to work together.

    This Is Not a New Model

    Civilian contractor involvement in the region also has a long history.

    During Plan Colombia, Congress specifically established personnel ceilings that included U.S. citizen civilian contractors. A State Department fact sheet from 2001 documented a statutory ceiling of 300 U.S. citizen civilian contractors, alongside limits on U.S. military personnel. The U.S. Embassy in Bogotá tracked contractor and military personnel numbers and activities for congressional reporting. [7]

    The historical personnel ceiling is not a description of today’s contracting environment. Its importance is that it demonstrates how formally civilian contractor support had already been incorporated into U.S. policy and oversight in the region more than two decades ago.

    Today, the regulatory framework is considerably more developed.

    For Department of Defense contracts, the DFARS includes specific rules for contractor personnel supporting U.S. Armed Forces deployed overseas. Depending on the mission and contract, requirements can include personnel accountability, predeployment requirements, country or theater clearance, security training, medical readiness, visas and entry documentation, and compliance with Combatant Command and Chief of Mission policies. [8]

    FAR 52.225-19 also makes an operational point that contractors cannot overlook: unless the contract says otherwise, the contractor is responsible for the logistical and security support required for its personnel. [1]

    That changes how an overseas project must be planned.

    The Contractor’s Job Is Often Integration

    A communications system is not useful merely because the hardware arrived.

    It must be transported, powered, configured, secured, connected, tested, documented, maintained, and supported by personnel who can operate in the local environment.

    The same applies to IT and operational technology.

    A successful contractor may need to integrate:

    • satellite communications;
    • terrestrial Internet;
    • fiber infrastructure;
    • wireless networks;
    • VHF/UHF communications;
    • secure routing and switching;
    • cybersecurity controls;
    • cloud and local applications;
    • AI-enabled tools and automation;
    • user devices;
    • power and environmental systems;
    • equipment logistics;
    • technical personnel; and
    • ongoing maintenance.

    The distinction between providing equipment and delivering an operational capability is critical.

    Federal procurement in the SOUTHCOM environment reflects this continued demand for technology services. For example, a 2026 SOUTHCOM-related award for enterprise data and analytics services carried a potential value of approximately $82.6 million and was classified under IT and computer-related services. [9]

    SOUTHCOM itself states that it is investing in command and control, logistics, sustainment, advanced systems, unmanned platforms, cybersecurity, and artificial intelligence while working with the defense industrial base and regional partners. [3]

    The technical-support requirement in the region is therefore broad—and becoming more integrated, not less.

    Where JPI Worldwide Fits

    For a prime contractor operating in the SOUTHCOM area of responsibility, one of the persistent challenges is finding subcontractors that can bridge the gap between engineering and deployment.

    A design created in the United States still has to work when it reaches the field.

    That is the problem set JPI Worldwide is structured to support.

    Communications and network infrastructure

    JPI can support projects involving fiber, wireless networking, VHF/UHF communications, satellite connectivity, Starlink and other broadband technologies, network engineering, and the supporting infrastructure necessary to establish communications in difficult environments.

    The objective is not simply connectivity. It is deployable, supportable connectivity appropriate to the mission and location.

    Systems and AI integration

    Modern government projects increasingly involve systems that span hardware, software, communications networks, cloud services, operational data, automation, and AI-enabled tools.

    JPI can work with a prime contractor to integrate those components into a functioning technical environment rather than treating each as an isolated product.

    Cybersecurity

    Deploying connectivity creates an attack surface.

    Networking, remote access, operational systems, cloud integration, endpoint technology, and AI-enabled platforms must therefore be considered together with cybersecurity requirements from the beginning of the project rather than added after deployment.

    Technical staffing and field services

    Overseas projects frequently require more than engineering documentation. They require people who can deploy, install, troubleshoot, train users, maintain systems, coordinate with other contractors, and remain engaged after initial installation.

    That field-support component can be especially valuable to a prime contractor that has program-management capacity but does not want to build a permanent technical workforce in every country where it performs.

    Logistics and deployment support

    Equipment does not install itself.

    International projects can involve procurement, staging, shipping, customs, inland transportation, deployment scheduling, field inventory, spare equipment, replacement parts, local coordination, and the movement of technical personnel.

    The Haiti Logistics Support Area is a large-scale example of the larger principle: mission capability depends on sustainment as much as initial deployment. [5][6]

    A Subcontractor Should Reduce Operational Friction

    For a government prime, the value of a mission-support subcontractor should ultimately be measured in reduced operational friction.

    The subcontractor should be able to take responsibility for a defined technical problem and move it from:

    requirement → design → procurement → integration → deployment → operation → sustainment.

    That becomes particularly important in Latin America and the Caribbean, where individual projects can combine long distances, limited infrastructure, difficult terrain, severe weather, language and regulatory considerations, and geographically distributed teams.

    The U.S. government’s own contracting rules recognize the reality of those operating conditions. FAR provisions governing overseas contractor personnel specifically contemplate work in dangerous or austere conditions, and require planning around personnel, logistics, security, clearances, transportation, and legal compliance. [1]

    For contractors working in the SOUTHCOM AOR, technical capability is only part of the requirement.

    The system has to work when it gets there.

    That is where an experienced technical and field-support partner can make the difference.


    Sources

    [1] Federal Acquisition Regulation, 52.225-19 — “Contractor Personnel in a Designated Operational Area or Supporting a Diplomatic or Consular Mission Outside the United States.”
    U.S. General Services Administration / Acquisition.gov, current FAR FAC 2026-01. FAR 52.225-19

    [2] U.S. Southern Command — About SOUTHCOM.
    Description of SOUTHCOM’s geographic responsibilities and command structure. U.S. Southern Command — About

    [3] U.S. Southern Command — Commander’s Imperatives / Innovating for Today’s Challenges.
    Current command priorities including command and control, logistics, sustainment, modernization, cybersecurity and regional partnerships. SOUTHCOM Commander’s Imperatives

    [4] U.S. Southern Command — Strengthening Defense and Security Partnerships in the Western Hemisphere. SOUTHCOM Defense and Security Partnerships

    [5] U.S. Department of State — Briefing by Assistant Secretary for Western Hemisphere Affairs Brian A. Nichols, September 2024.
    Describes DoD funding and contractor construction/operation of the Haiti logistics support area.

    [6] U.S. Department of State — 2025 Report to Congress on Progress Implementing the U.S. Strategy to Prevent Conflict and Promote Stability.
    Describes DoD sustainment contracts supporting Haiti operations, including billeting, sanitation, food, maintenance and mission-planning facilities.

    [7] U.S. Department of State — “Civilian Contractors and U.S. Military Personnel Supporting Plan Colombia,” May 15, 2001. State Department Plan Colombia contractor fact sheet

    [8] Defense Federal Acquisition Regulation Supplement, Subpart 225.3 — Contracts Performed Outside the United States. DFARS Subpart 225.3

    [9] SAM.gov — USSOUTHCOM J2 EDA IDIQ, Award W91QEX26DA003.
    Federal award information documenting an approximately $82.6 million ceiling for SOUTHCOM-related IT and enterprise data/analytics services.